George Bailey

George Bailey is a cybersecurity researcher and writer at CyberExperts, covering cyber threats, AI, cloud security, vulnerabilities, and defensive strategies. His goal is to help security professionals quickly understand what matters most and how it impacts their organizations.

The 5-Minute Cyber Brief: September 11, 2026

The 5-Minute Cyber Brief: September 11, 2026

Published: 09/11/26 Today’s pattern is management-plane root: when the systems that configure firewalls, terminate VPN, and run ERP kernels become…

SAP OVERPASS CVE-2026-44756: unauth OS command exec on NetWeaver/Web Dispatcher

SAP OVERPASS CVE-2026-44756: unauth OS command exec on NetWeaver/Web Dispatcher

What Changed SAP’s September 2026 Patch Day, with Onapsis Research Labs, shipped Security Note 3747649 for OVERPASS (CVE-2026-44756): a memory-corruption…

Check Point twin CVSS 9.8s in VPN certificate path (CVE-2026-85102 / 85103)

Check Point twin CVSS 9.8s in VPN certificate path (CVE-2026-85102 / 85103)

What Changed Check Point disclosed on September 9, 2026 two critical flaws in VPN certificate handling on Quantum Security Gateway…

Fortinet CVE-2025-25249: PivotC2 Node.js RAT on FortiGate after cw_acd RCE

Fortinet CVE-2025-25249: PivotC2 Node.js RAT on FortiGate after cw_acd RCE

What Changed SOCRadar reports that Russian-speaking cybercrime actors have been exploiting CVE-2025-25249—an unauthenticated heap-based buffer overflow in the FortiOS and…

Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

What Changed Cisco Talos confirmed on September 9–10 that three intrusion clusters are actively abusing Cisco Secure Firewall Management Center…

The 5-Minute Cyber Brief: September 10, 2026

The 5-Minute Cyber Brief: September 10, 2026

BlueMoon’s shared Chrome kit, Kestra’s suffix-match RCE, LiteLLM’s empty MCP session, and Windows Update Stack’s SYSTEM zero-day....

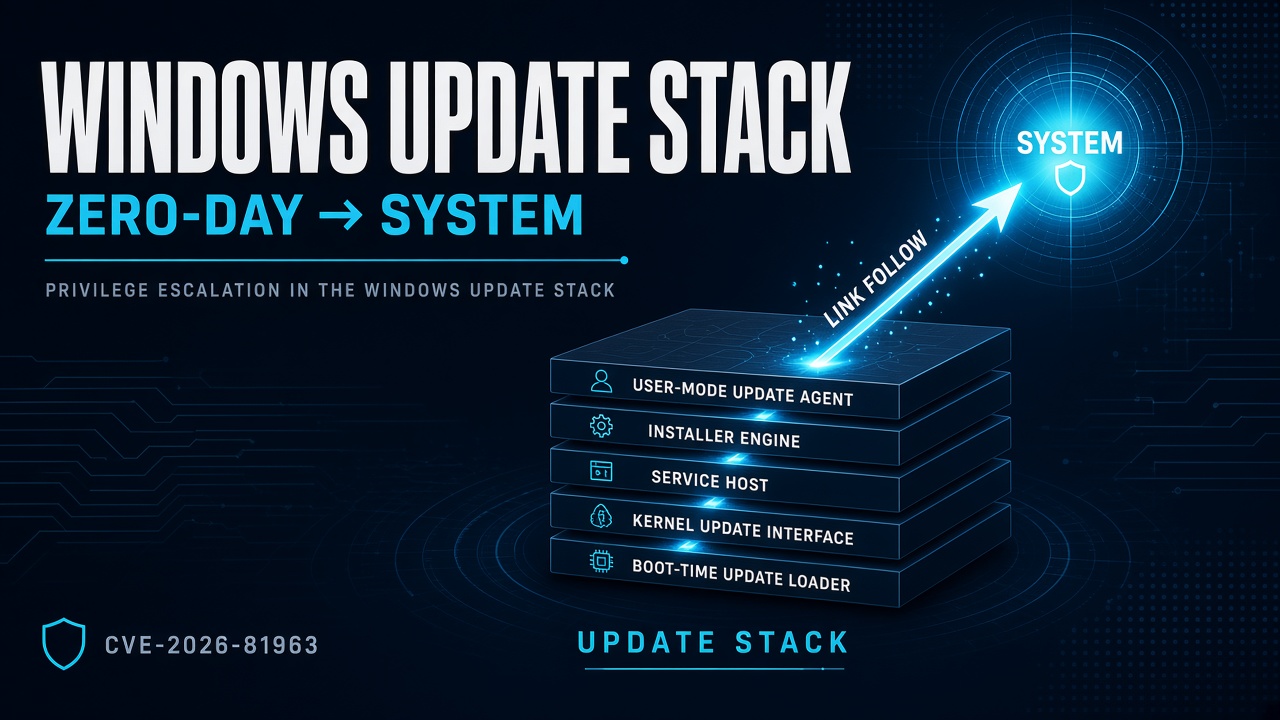
Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

September Patch Tuesday’s exploited Update Stack EoP turns a low-privilege foothold into SYSTEM—and it is already in KEV....

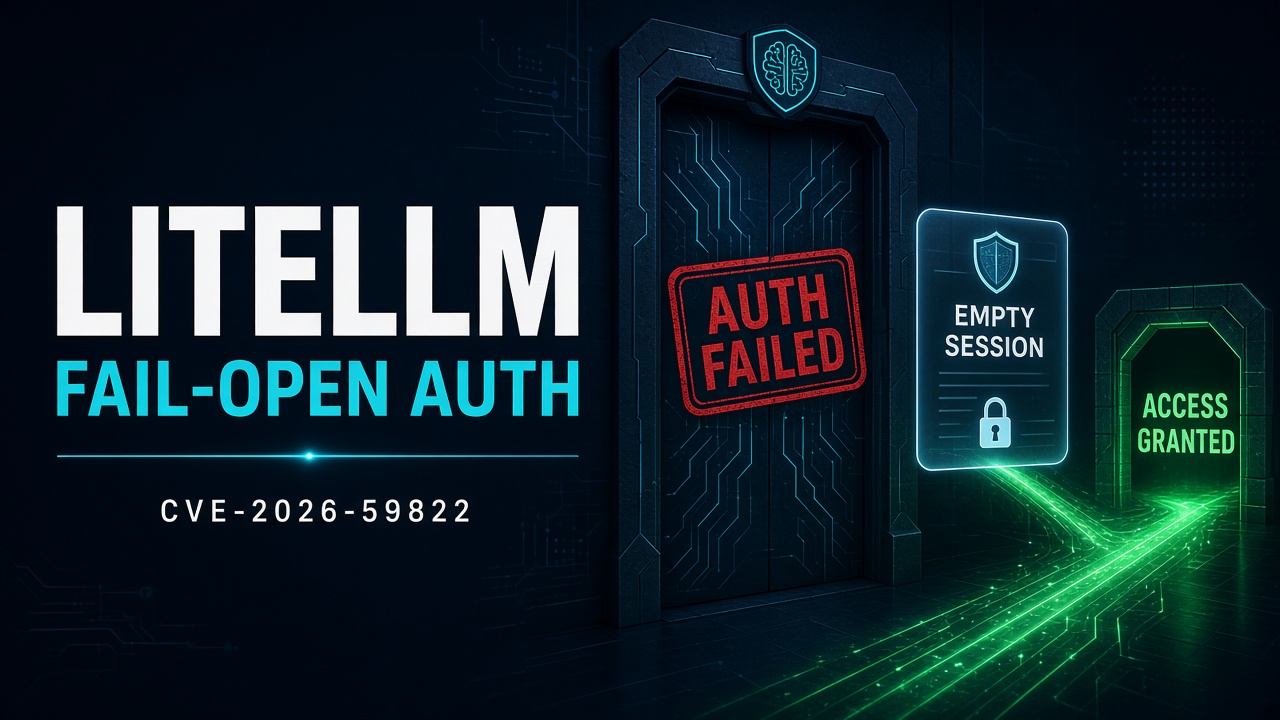
LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

Before 1.84.0, LiteLLM’s MCP path could replace a failed Bearer check with an empty UserAPIKeyAuth()—and CISA put it in KEV....

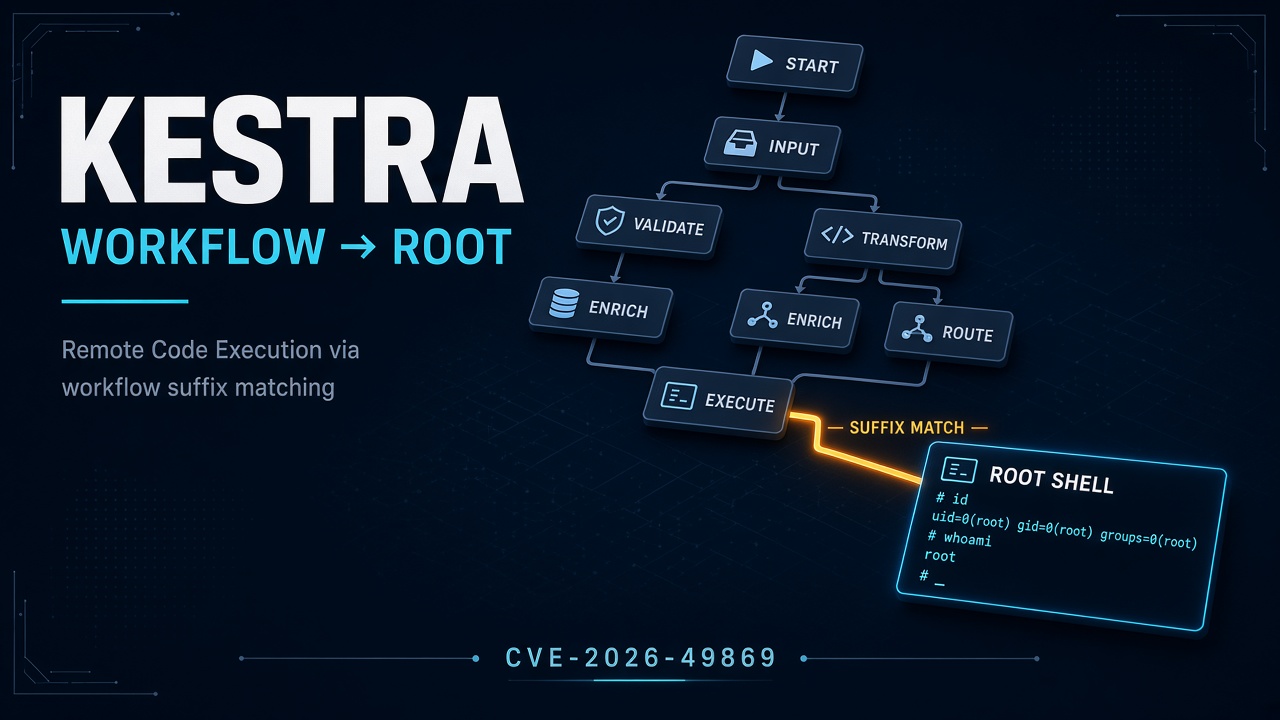
Kestra CVE-2026-49869: The Suffix Match That Turned Workflows Into Root Shells

Kestra CVE-2026-49869: The Suffix Match That Turned Workflows Into Root Shells

CVE-2026-49869 (CVSS 10.0) lets unauthenticated attackers bypass Kestra Basic Auth with any path ending in /configs and run root workflows....

BlueMoon: Four Espionage Groups Share One Chrome-to-SYSTEM Exploit Kit

BlueMoon: Four Espionage Groups Share One Chrome-to-SYSTEM Exploit Kit

Proofpoint’s BlueMoon kit chains Chromium patch-gap RCE with a Windows ALPC LPE—and four espionage clusters adopted it in days....

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

CVE-2026-19490 is a CVSS 9.3 NetScaler Gateway/AAA auth bypass. A public PoC on Sept 2 was followed by live probes…

The 5-Minute Cyber Brief: September 9, 2026

The 5-Minute Cyber Brief: September 9, 2026

SonicWall SMA1000 unauthenticated RCE, JFrog Artifactory phantom join-key admin tokens, and PaperCut’s second emergency patch—control-plane risk explained in about five…

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

CVE-2026-81578 and CVE-2026-82078 chain to pre-auth RCE on PaperCut Application Server. Confirm Emergency Patch Release 2, restrict admin exposure, and…