Cyber News

Inside the Daily Brief

A real sample of the weekday read

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

CVE-2026-19490 is a CVSS 9.3 NetScaler Gateway/AAA auth bypass. A public PoC on Sept 2 was followed by live probes…

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

CVE-2026-81578 and CVE-2026-82078 chain to pre-auth RCE on PaperCut Application Server. Confirm Emergency Patch Release 2, restrict admin exposure, and…

JFrog Artifactory CVE-2026-82329: Empty Join Key, Full Admin Token, Busy Scanners

JFrog Artifactory CVE-2026-82329: Empty Join Key, Full Admin Token, Busy Scanners

CVE-2026-82329 lets attackers forge Artifactory admin tokens via a deterministic empty join key. Mass scanning peaked near 406,000 attempts; patch…

The CyberExperts Daily Brief

Keep up with the cyber news that changes the day

Get the weekday brief for people scanning the news: the developments worth a closer look, explained in about five minutes.

SonicWall SMA1000: The Front Door Had a Side Door, and Attackers Used Both

SonicWall SMA1000: The Front Door Had a Side Door, and Attackers Used Both

CVE-2026-83548 and CVE-2026-83549 chain pre-auth SSRF into AMC command injection for unauthenticated RCE on SonicWall SMA1000 gateways. Patch 12.4.3-03526 /…

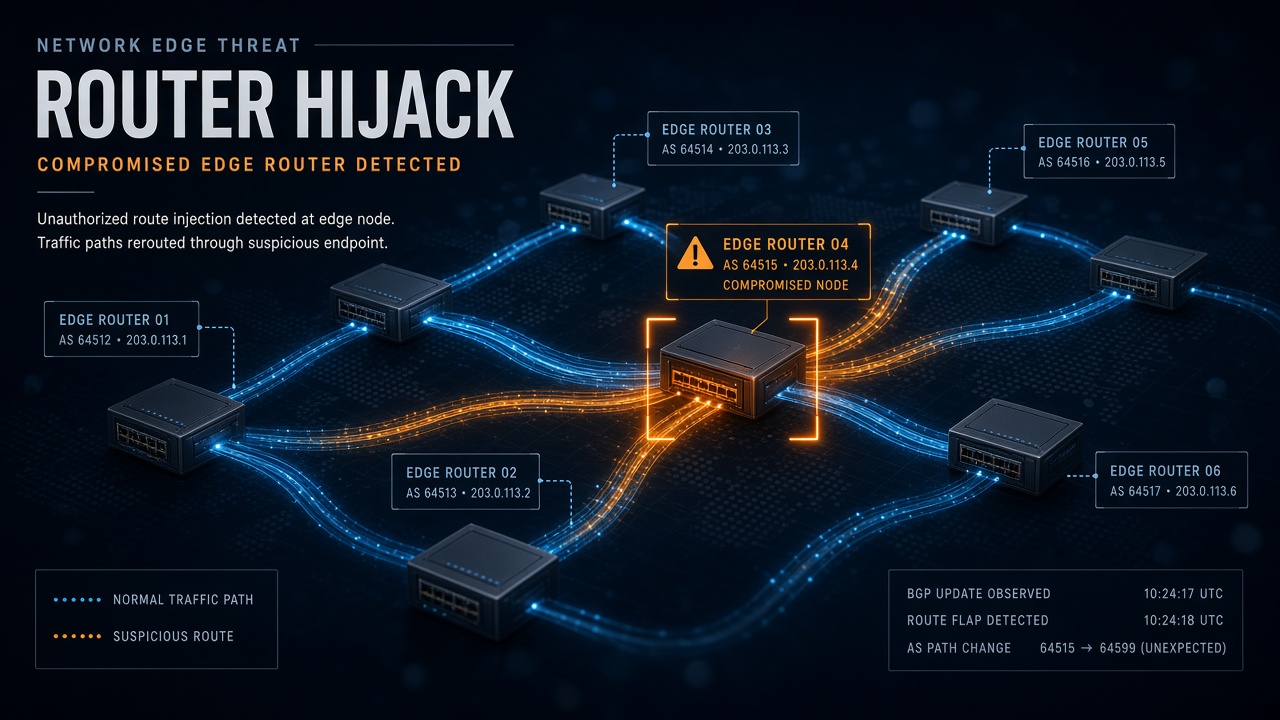
MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

What Changed Poland’s CERT.PL is warning that attackers are actively exploiting a chain of MikroTik RouterOS vulnerabilities it calls MikroTrick.…

N-able N-central CVE-2026-86218: Pre-Auth RCE Puts MSP Customers in the Blast Radius

N-able N-central CVE-2026-86218: Pre-Auth RCE Puts MSP Customers in the Blast Radius

What Changed N-able released an emergency fix for CVE-2026-86218, a critical vulnerability in N-central that can allow pre-authenticated remote code…

StyleSmuggler: Magento and Adobe Commerce CVSS 10.0 RCE Is Under Active Attack

StyleSmuggler: Magento and Adobe Commerce CVSS 10.0 RCE Is Under Active Attack

What Changed Sansec has disclosed an unauthenticated remote-code-execution chain in Magento and Adobe Commerce that it calls StyleSmuggler. Adobe tracks…

Coder’s registry infrastructure compromised to push malicious modules

Coder’s registry infrastructure compromised to push malicious modules

The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no…

Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks

Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks

The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes…

HPE patches critical ArubaOS-CX remote code execution flaw

HPE patches critical ArubaOS-CX remote code execution flaw

ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation…

Thomson Reuters Court Software Breach May Have Exposed SSNs and Sealed Data

Thomson Reuters Court Software Breach May Have Exposed SSNs and Sealed Data

The C-Track story matters because it sits inside judicial workflow, not generic office software. When court case-management data is exposed,…

Critical Cisco Nexus 9000 Flaw Lets Unauthenticated Remote Attackers Run Code as Root

Critical Cisco Nexus 9000 Flaw Lets Unauthenticated Remote Attackers Run Code as Root

Cisco's Nexus 9000 update is the kind of network-infrastructure issue that should not wait behind normal maintenance rhythm. The core…

“Sorry, I can’t help with that”: How your guardrails might become the attacker’s best friend

“Sorry, I can’t help with that”: How your guardrails might become the attacker’s best friend

Cisco Talos is making a more practical point than the headline alone suggests: if defensive workflows depend on third-party AI…