George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
The 5-Minute Cyber Brief: September 14, 2026

The 5-Minute Cyber Brief: September 14, 2026

Monday due dates: GitLab file-read, ScreenConnect client, Chrome’s seventh 2026 zero-day, WatchGuard ransomware flag....

WatchGuard Firebox CVE-2025-14733: CISA Flags Ransomware Use on a Stubborn Edge RCE

WatchGuard Firebox CVE-2025-14733: CISA Flags Ransomware Use on a Stubborn Edge RCE

CISA marked the WatchGuard Firebox RCE as known ransomware campaign use. Patch the edge....

Chrome CVE-2026-87491: Google’s Seventh Exploited Zero-Day of 2026 — Update to 153

Chrome CVE-2026-87491: Google’s Seventh Exploited Zero-Day of 2026 — Update to 153

Google patched a V8 bug already exploited in the wild. Chrome 153 is the floor....

ConnectWise ScreenConnect CVE-2026-84869: Guest Session, Host Compromise — KEV Due Today

ConnectWise ScreenConnect CVE-2026-84869: Guest Session, Host Compromise — KEV Due Today

A ScreenConnect client bug can transfer and run files on the host without confirmation. Due today....

GitLab CVE-2026-85706: One Request, No Login, Your Secrets on Disk — Patch Deadline Is Today

GitLab CVE-2026-85706: One Request, No Login, Your Secrets on Disk — Patch Deadline Is Today

Self-hosted GitLab: one unauthenticated commits-API request can read secrets on disk. Federal due date is today....

The 5-Minute Cyber Brief: September 11, 2026

The 5-Minute Cyber Brief: September 11, 2026

Published: 09/11/26 Today’s pattern is management-plane root: when the systems that configure firewalls, terminate VPN, and run ERP kernels become…

SAP OVERPASS CVE-2026-44756: unauth OS command exec on NetWeaver/Web Dispatcher

SAP OVERPASS CVE-2026-44756: unauth OS command exec on NetWeaver/Web Dispatcher

OVERPASS: pre-auth memory corruption in the SAP kernel SAP’s September 2026 Patch Day, with Onapsis Research Labs, shipped Security Note…

Check Point twin CVSS 9.8s in VPN certificate path (CVE-2026-85102 / 85103)

Check Point twin CVSS 9.8s in VPN certificate path (CVE-2026-85102 / 85103)

Two CVSS 9.8 bugs in VPN certificate parsing Check Point disclosed on September 9, 2026 two critical flaws in VPN…

Fortinet CVE-2025-25249: PivotC2 Node.js RAT on FortiGate after cw_acd RCE

Fortinet CVE-2025-25249: PivotC2 Node.js RAT on FortiGate after cw_acd RCE

What Changed SOCRadar reports that Russian-speaking cybercrime actors have been exploiting CVE-2025-25249, an unauthenticated heap-based buffer overflow in the FortiOS…

Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

What Changed Cisco Talos confirmed on September 9–10 that three intrusion clusters are actively abusing Cisco Secure Firewall Management Center…

The 5-Minute Cyber Brief: September 10, 2026

The 5-Minute Cyber Brief: September 10, 2026

BlueMoon’s shared Chrome kit, Kestra’s suffix-match RCE, LiteLLM’s empty MCP session, and Windows Update Stack’s SYSTEM zero-day....

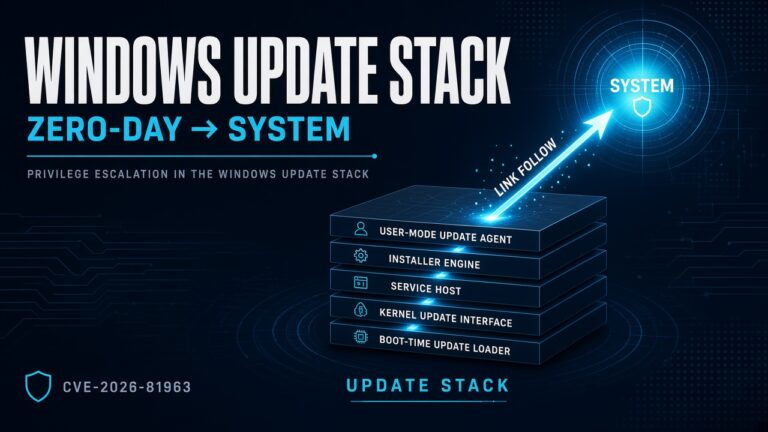
Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

September Patch Tuesday’s exploited Update Stack EoP turns a low-privilege foothold into SYSTEM—and it is already in KEV....

LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

Before 1.84.0, LiteLLM’s MCP path could replace a failed Bearer check with an empty UserAPIKeyAuth()—and CISA put it in KEV....