George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution

The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution

Unit 42's AI-enabled malware dataset is useful because it cuts through hype with numbers: 405 samples collected, only 12 observed…

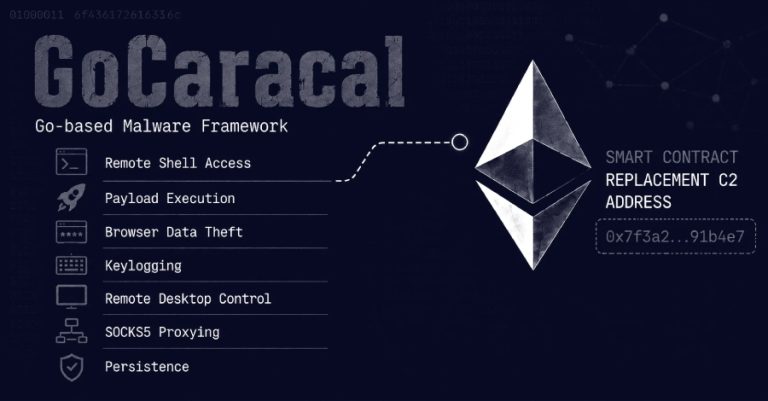
GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address

GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address

Arctic Wolf's GoCaracal research is useful because it adds specifics to the Dark Caracal story: a Go-based framework with lightweight…

Critical Avada WordPress theme flaw enables zero-click RCE

Critical Avada WordPress theme flaw enables zero-click RCE

CVE-2026-18431 is not a simple plugin bug. Wordfence says attackers can chain six weaknesses across the Avada theme and Fusion…

Hackers target Microsoft SharePoint RCE chain with PoC exploit

Hackers target Microsoft SharePoint RCE chain with PoC exploit

The SharePoint story is more specific than "RCE chain under attack." Defenders are now dealing with CVE-2026-55040 in the JWT…

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday

CVE-2026-8452 is no longer a theoretical NetScaler problem. CISA has now ordered federal agencies to fix it by August 29…

The 5-Minute Cyber Brief: August 26, 2026

The 5-Minute Cyber Brief: August 26, 2026

The cybersecurity developments that matter most today, explained in about five minutes....

E4del and PINHOLE RATs Turn FTP Banners Into Dead Drops for Malware Commands

E4del and PINHOLE RATs Turn FTP Banners Into Dead Drops for Malware Commands

This campaign is worth attention because it moves dead-drop logic into an FTP welcome banner, which is unusual enough to…

The safety penalty: Reclaiming operational sovereignty in the age of AI

The safety penalty: Reclaiming operational sovereignty in the age of AI

Cisco Talos is making a strategic point that security leaders should not dismiss as thought-leadership filler. If defensive workflows depend…

AnonyMousKIT PhaaS uses voice AI agents to phish iPhone passcodes

AnonyMousKIT PhaaS uses voice AI agents to phish iPhone passcodes

AnonyMousKIT is more than another phishing-kit story because it connects stolen-device monetization to identity abuse. The useful operator detail is…

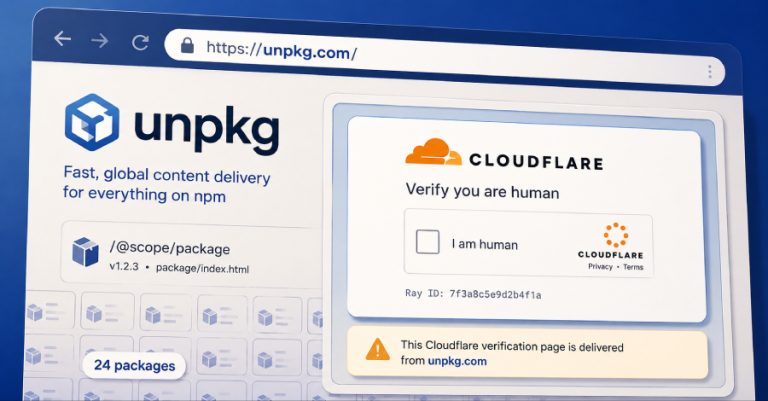
24 npm Packages Abuse unpkg Mirrors to Host Fake Cloudflare CAPTCHA Pages

24 npm Packages Abuse unpkg Mirrors to Host Fake Cloudflare CAPTCHA Pages

This campaign matters because the attacker is abusing trusted software-distribution infrastructure rather than only throwaway phishing sites. The useful detail…

Hackers breached over 270 Zimbra servers in ongoing attacks

Hackers breached over 270 Zimbra servers in ongoing attacks

Shadowserver found 274 Zimbra servers compromised through CVE-2026-73570 and at least 8,200 unpatched. Upgrade to ZCS 10.1.20 and hunt for…

The 5-Minute Cyber Brief: August 25, 2026

The 5-Minute Cyber Brief: August 25, 2026

Live Zimbra exploitation, WordPress SSO abuse, a Keycloak takeover bug, and a router flaw that punches through NAT....

Critical Keycloak Password Reset Flaw Could Let Unauthenticated Attackers Take Over Any Account

Critical Keycloak Password Reset Flaw Could Let Unauthenticated Attackers Take Over Any Account

Keycloak CVE-2026-18963 deserves attention because it attacks the recovery path defenders usually trust when something else goes wrong. If an…