George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

Cisco FMC CVE-2026-20079: Sandworm-linked and Qilin clusters hit firewall management for root

What Changed Cisco Talos confirmed on September 9–10 that three intrusion clusters are actively abusing Cisco Secure Firewall Management Center…

The 5-Minute Cyber Brief: September 10, 2026

The 5-Minute Cyber Brief: September 10, 2026

BlueMoon’s shared Chrome kit, Kestra’s suffix-match RCE, LiteLLM’s empty MCP session, and Windows Update Stack’s SYSTEM zero-day....

Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

Windows Update Stack CVE-2026-81963: The Link-Following Zero-Day That Finishes the Job

September Patch Tuesday’s exploited Update Stack EoP turns a low-privilege foothold into SYSTEM—and it is already in KEV....

LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

LiteLLM CVE-2026-59822: Failed Auth Fell Through to an Empty MCP Session

Before 1.84.0, LiteLLM’s MCP path could replace a failed Bearer check with an empty UserAPIKeyAuth()—and CISA put it in KEV....

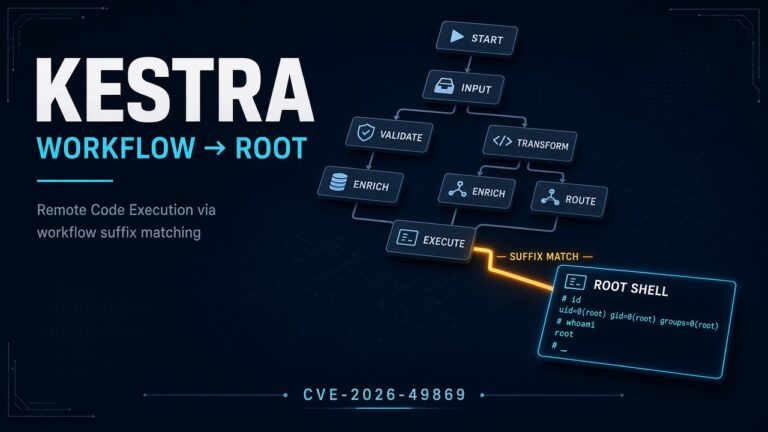
Kestra CVE-2026-49869: The Suffix Match That Turned Workflows Into Root Shells

Kestra CVE-2026-49869: The Suffix Match That Turned Workflows Into Root Shells

CVE-2026-49869 (CVSS 10.0) lets unauthenticated attackers bypass Kestra Basic Auth with any path ending in /configs and run root workflows....

BlueMoon: Four Espionage Groups Share One Chrome-to-SYSTEM Exploit Kit

BlueMoon: Four Espionage Groups Share One Chrome-to-SYSTEM Exploit Kit

Proofpoint’s BlueMoon kit chains Chromium patch-gap RCE with a Windows ALPC LPE—and four espionage clusters adopted it in days....

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

Citrix NetScaler CVE-2026-19490: The Auth Bypass That Went From PoC to Probes in a Day

CVE-2026-19490 is a CVSS 9.3 NetScaler Gateway/AAA auth bypass. A public PoC on Sept 2 was followed by live probes…

The 5-Minute Cyber Brief: September 9, 2026

The 5-Minute Cyber Brief: September 9, 2026

SonicWall SMA1000 unauthenticated RCE, JFrog Artifactory phantom join-key admin tokens, and PaperCut’s second emergency patch—control-plane risk explained in about five…

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

PaperCut NG/MF: The Print Server That Learned Remote Code Execution Again

CVE-2026-81578 and CVE-2026-82078 chain to pre-auth RCE on PaperCut Application Server. Confirm Emergency Patch Release 2, restrict admin exposure, and…

JFrog Artifactory CVE-2026-82329: Empty Join Key, Full Admin Token, Busy Scanners

JFrog Artifactory CVE-2026-82329: Empty Join Key, Full Admin Token, Busy Scanners

CVE-2026-82329 lets attackers forge Artifactory admin tokens via a deterministic empty join key. Mass scanning peaked near 406,000 attempts; patch…

SonicWall SMA1000: The Front Door Had a Side Door, and Attackers Used Both

SonicWall SMA1000: The Front Door Had a Side Door, and Attackers Used Both

CVE-2026-83548 and CVE-2026-83549 chain pre-auth SSRF into AMC command injection for unauthenticated RCE on SonicWall SMA1000 gateways. Patch 12.4.3-03526 /…

The 5-Minute Cyber Brief: September 8, 2026

The 5-Minute Cyber Brief: September 8, 2026

Today’s stories share one pattern: commerce platforms that hold payment and customer data, MSP toolchains that administer many environments, and…

MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

CERT.PL: the MikroTrick chain turns exposed SSH into router admin Poland’s CERT.PL is warning that attackers are actively exploiting a…