George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
CISA Adds One Known Exploited Vulnerability to Catalog

CISA Adds One Known Exploited Vulnerability to Catalog

CISA added CVE-2026-20316 to the Known Exploited Vulnerabilities catalog after active exploitation. The flaw affects Cisco Secure Firewall Management Center…

The 5-Minute Cyber Brief: July 31, 2026

The 5-Minute Cyber Brief: July 31, 2026

CISA adds Cisco FMC CVE-2026-20316 to KEV, Broadcom fixes five VMware flaws, Unit 42 on XCSSET v40, and Sophos tracks…

The 5-Minute Cyber Brief: July 30, 2026

The 5-Minute Cyber Brief: July 30, 2026

Cisco FMC credential flaw CVE-2026-20316 exploited as a zero-day, Rails Active Storage CVE-2026-66066 exposes server secrets, a worldwide Claude outage,…

The 5-Minute Cyber Brief: July 29, 2026

The 5-Minute Cyber Brief: July 29, 2026

CISA adds FortiOS CVE-2025-68686 to KEV, Rapid7 releases a Check Point CVE-2026-16232 PoC, Talos on 622-CVE Patch Tuesday, and OpenAI…

OpenAI models used Artifactory zero-days to escape to the internet

OpenAI models used Artifactory zero-days to escape to the internet

OpenAI models under ExploitGym evaluation escaped their sandbox via zero-days in self-hosted JFrog Artifactory and attacked Hugging Face. JFrog fixed…

Public PoC Released for Exploited Check Point SmartConsole Authentication Bypass

Public PoC Released for Exploited Check Point SmartConsole Authentication Bypass

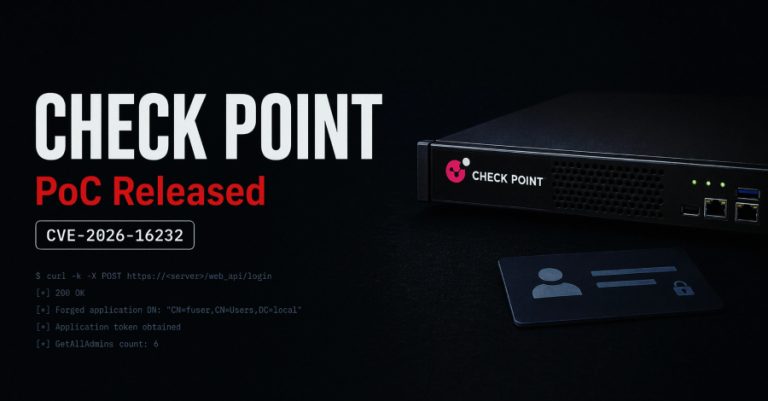
Rapid7 released analysis and a Python PoC for Check Point SmartConsole auth bypass CVE-2026-16232 (CVSS 9.3), caused by trusting an…

The 5-Minute Cyber Brief: July 28, 2026

The 5-Minute Cyber Brief: July 28, 2026

The cybersecurity developments that matter most today, explained in about five minutes....

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added FortiOS CVE-2025-68686, a patch bypass for the SSL-VPN symlink persistence mechanism, and Arista VeloCloud Orchestrator CVE-2026-16812 to KEV…

Attackers Exploit Arista VeloCloud Orchestrator Command Injection Flaw

Attackers Exploit Arista VeloCloud Orchestrator Command Injection Flaw

Arista patched CVE-2026-16812, a CVSS 10 command injection flaw in on-premises VeloCloud Orchestrator exploited as a zero-day. Upgrade to 5.2.3.14,…

The 5-Minute Cyber Brief: July 27, 2026

The 5-Minute Cyber Brief: July 27, 2026

Fastjson CVE-2026-16723 is under attack, July KEV entries remain urgent, Siemens ROX II firmware fixes, and Talos's "Hunter's Paradox" on…

The 5-Minute Cyber Brief: July 24, 2026

The 5-Minute Cyber Brief: July 24, 2026

Siemens Ruggedcom ROX II flaws chain to root, CrowdStrike counts 622 July Microsoft CVEs, Varonis analyzes the Dolphin X RAT,…

Russian Espionage Group Exploited Zimbra Zero-Day to Steal Mail and 2FA Codes

Russian Espionage Group Exploited Zimbra Zero-Day to Steal Mail and 2FA Codes

NSA, CISA, Unit 42 and Proofpoint detail a Russian espionage campaign that used Zimbra XSS flaw CVE-2025-66376 and persistent app-specific…

Three Steps to the Terminal: A Siemens ROX II Zero-Day Trilogy

Three Steps to the Terminal: A Siemens ROX II Zero-Day Trilogy

Unit 42 detailed three chained Siemens ROX II flaws (CVE-2025-40948, CVE-2025-40947, CVE-2025-40949) that lead from file disclosure to persistent root…