George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
Attackers Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets

Attackers Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets

Attackers are exploiting an MLflow SSRF flaw to reach cloud metadata services and steal credentials, while a separate FUXA issue…

Clop created custom web shell for Windchill data theft attacks

Clop created custom web shell for Windchill data theft attacks

ReliaQuest found a custom Clop web shell for PTC Windchill and FlexPLM, used via CVE-2026-12569 to locate and steal design…

CISA: Windows Task Host flaw now exploited by ransomware gangs

CISA: Windows Task Host flaw now exploited by ransomware gangs

CISA now flags Windows Task Host privilege escalation flaw CVE-2025-60710, patched in November 2025, as used in ransomware attacks. Check…

The 5-Minute Cyber Brief: August 18, 2026

The 5-Minute Cyber Brief: August 18, 2026

ShieldBreak still unpatched, GitLab fixes critical CVE-2026-19478, Pokémon Center data exposed via CEVA, Microsoft on DeadLock ransomware, and August's network…

Pokémon Center data breach exposes customer info, cancels some orders

Pokémon Center data breach exposes customer info, cancels some orders

Pokémon Center UK and Germany customer names, addresses, phone numbers, emails and orders were exposed in the CEVA Logistics breach.…

SAP Commerce Cloud CVE-2026-58231 Targeted in Exploitation Attempts Days After Patch

SAP Commerce Cloud CVE-2026-58231 Targeted in Exploitation Attempts Days After Patch

Attackers began probing SAP Commerce Cloud flaw CVE-2026-58231 (CVSS 10) three days after the patch. Onapsis advises patching, then rebuilding…

Microsoft working on Defender patch for ShieldBreak zero-day

Microsoft working on Defender patch for ShieldBreak zero-day

Microsoft is working on a patch for ShieldBreak, a public Defender zero-day (CVE-2026-69414) that bypasses the RoguePlanet fix and gives…

The 5-Minute Cyber Brief: August 17, 2026

The 5-Minute Cyber Brief: August 17, 2026

Microsoft prepares a fix for Defender zero-day ShieldBreak, SAP Commerce Cloud CVE-2026-58231 targeted days after patch, and August's critical DNS,…

New AmnesiaStealer macOS malware hijacks browser sessions via remote control

New AmnesiaStealer macOS malware hijacks browser sessions via remote control

AmnesiaStealer is worth a closer look because it is not just another Mac infostealer. Its operators pair ClickFix-style social engineering…

Max severity SAP Commerce Cloud flaw now targeted in attacks

Max severity SAP Commerce Cloud flaw now targeted in attacks

A max-severity SAP Commerce Cloud flaw being targeted only days after patch release should move this out of routine enterprise-app…

DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure

DeadLock ransomware: Breaking down a Rust-based encryptor with decentralized recovery infrastructure

DeadLock matters because Microsoft is describing more than another ransomware name. The operation uses decentralized infrastructure for communications, negotiation, and…

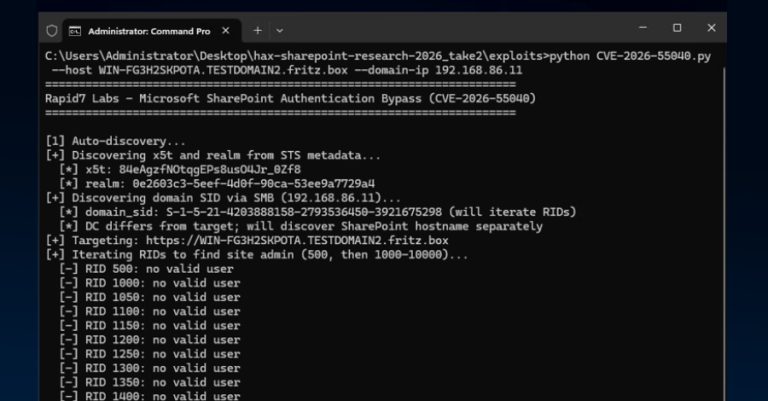
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

A SharePoint authentication bypass becomes much more serious once public proof-of-concept code and real exploitation arrive together. At that point,…

Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy Backdoor

Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy Backdoor

A Lazarus-linked Windows zero-day is not routine vulnerability noise. It is the kind of story that forces defenders to treat…