George Bailey

George Bailey is a cybersecurity researcher and writer at CyberExperts, covering cyber threats, AI, cloud security, vulnerabilities, and defensive strategies. His goal is to help security professionals quickly understand what matters most and how it impacts their organizations.

The 5-Minute Cyber Brief: September 8, 2026

The 5-Minute Cyber Brief: September 8, 2026

The useful pattern today is shared blast radius: commerce platforms that hold payment and customer data, MSP toolchains that administer…

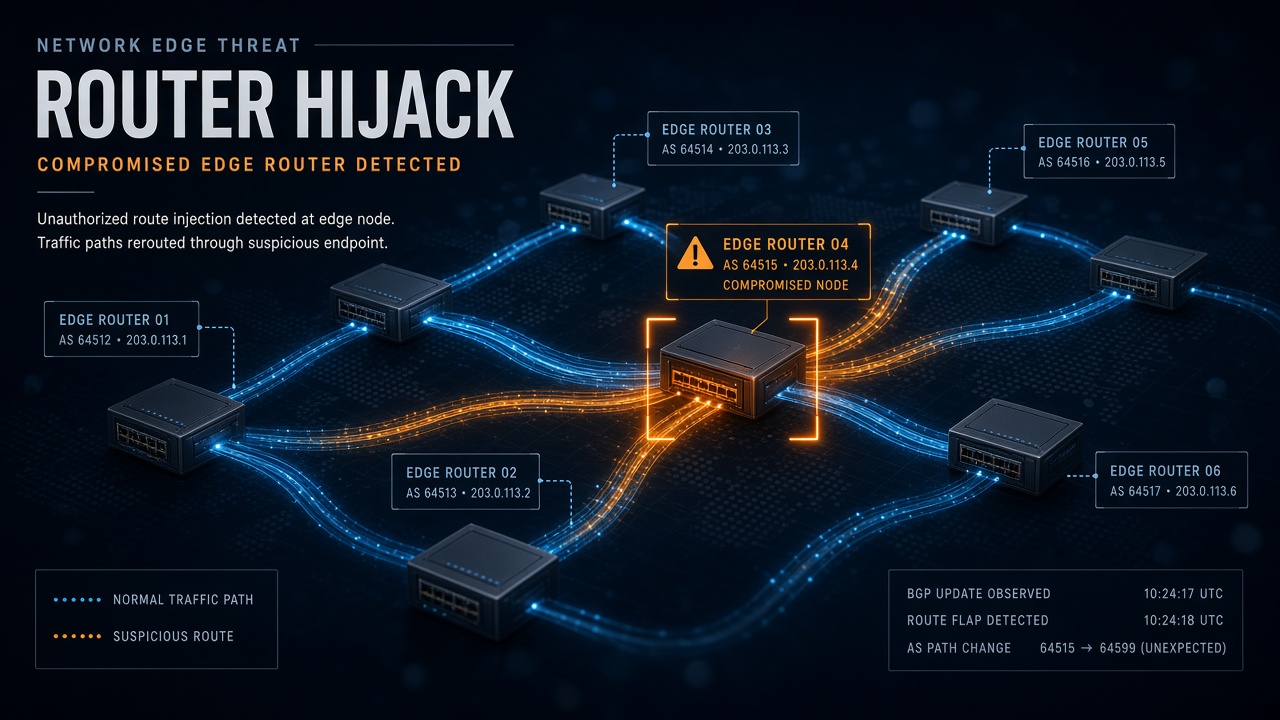
MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

MikroTrick: MikroTik RouterOS Flaws Are Hijacking Internet-Exposed Routers

What Changed Poland’s CERT.PL is warning that attackers are actively exploiting a chain of MikroTik RouterOS vulnerabilities it calls MikroTrick.…

N-able N-central CVE-2026-86218: Pre-Auth RCE Puts MSP Customers in the Blast Radius

N-able N-central CVE-2026-86218: Pre-Auth RCE Puts MSP Customers in the Blast Radius

What Changed N-able released an emergency fix for CVE-2026-86218, a critical vulnerability in N-central that can allow pre-authenticated remote code…

StyleSmuggler: Magento and Adobe Commerce CVSS 10.0 RCE Is Under Active Attack

StyleSmuggler: Magento and Adobe Commerce CVSS 10.0 RCE Is Under Active Attack

What Changed Sansec has disclosed an unauthenticated remote-code-execution chain in Magento and Adobe Commerce that it calls StyleSmuggler. Adobe tracks…

Nearly 22,000 Microsoft Exchange servers vulnerable to hijack attacks

Nearly 22,000 Microsoft Exchange servers vulnerable to hijack attacks

Nearly 22,000 Microsoft Exchange servers exposed online remain unpatched against a high-severity authentication bypass vulnerability that allows attackers to hijack…

Aesto Health says data breach affects over 9.5 million patients

Aesto Health says data breach affects over 9.5 million patients

Aesto LLC, operating as Aesto Health, disclosed that a data breach discovered recently affects more than 9.5 million individuals....

The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution

The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution

Unit 42's AI-enabled malware research is useful because it separates hype from operational change. The story is not that attackers…

Critical Langflow flaw exploited to steal OpenAI and AWS keys

Critical Langflow flaw exploited to steal OpenAI and AWS keys

Threat actors are exploiting an unauthenticated remote code execution vulnerability (CVE-2026-0768) in Langflow, an open-source framework for building AI applications,…

Attackers Exploit Critical JFrog Artifactory Flaw to Mint Admin Tokens Days After Disclosure

Attackers Exploit Critical JFrog Artifactory Flaw to Mint Admin Tokens Days After Disclosure

Threat actors are exploiting a newly patched critical security flaw impacting JFrog Artifactory merely days after public disclosure, according to…

Russia-Aligned UAC-0099 Plants Nuclear Weapon Prompt in Malware to Disrupt AI Analysis

Russia-Aligned UAC-0099 Plants Nuclear Weapon Prompt in Malware to Disrupt AI Analysis

Cybersecurity researchers have disclosed a new technique dubbed GuardBreaker that's been put to use by a Russia-aligned threat actor known…

August 2026 Patch Tuesday: One Exploited Zero-Day and 62 Critical Vulnerabilities Among 415 CVEs

August 2026 Patch Tuesday: One Exploited Zero-Day and 62 Critical Vulnerabilities Among 415 CVEs

CrowdStrike's August Patch Tuesday analysis matters because it turns a wall of Microsoft CVEs into a prioritization map. The real…

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA's latest KEV move matters because it turns two PaperCut flaws into an immediate exposure decision, not a routine backlog…

Identity Abuse Through Trusted Communication Channels

Identity Abuse Through Trusted Communication Channels

This Unit 42 research matters because it explains how identity attacks ride inside the tools employees already trust. The danger…