Inside the Daily Brief
Sep 24, 2026
The TrueConf compromise is not just a server-breach story. It is a reminder that update channels themselves become attack infrastructure…
CISA added Progress Kemp LoadMaster flaw CVE-2026-8037 to the KEV catalog after repeated exploitation attempts, turning a load balancer bug…
Metabase confirmed active exploitation of a critical unauthenticated SQL injection flaw that can hand a remote attacker administrator access to…
The CyberExperts Daily Brief
Get the weekday brief for people scanning the news: the developments worth a closer look, explained in about five minutes.
By subscribing you agree to our Privacy Policy. Weekday emails only.
CISA is telling federal agencies to move within three days on actively exploited flaws in IBM Langflow, N-able N-central, and…
A new class of prompt injection is spreading across commercial websites. It requires no malware, no stolen credentials, and no…
Unit 42 described three post-compromise attack paths against Chrome's Google Password Manager on Windows that could let malware bypass user-verification…
Analysis of XCSSET v40 reveals a macOS malware targeting developers via Xcode. Unit 42 used advanced pattern matching and AI…
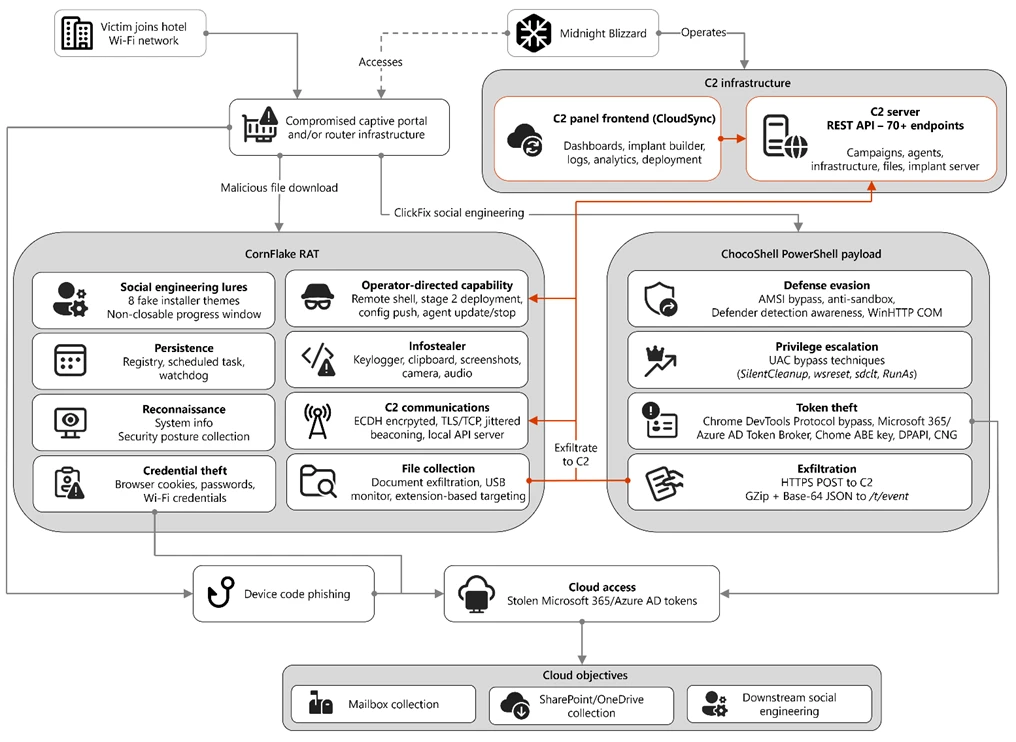
Storm-2945, a sub-cluster of the Russian threat actor Midnight Blizzard, has been observed compromising the sign-in portals of hospitality-related organizations…
A new Russian loader-as-a-service named DOUBLECUP uses ClickFix attacks to hide malicious code in PNG images cached by victims' browsers,…
The INC Ransomware operation has emerged as the "dominant threat actor" exploiting the recently disclosed security flaws in SonicWall Secure…
A technical analysis of three chained zero-day vulnerabilities in Siemens ROX II OT switches that allow privilege escalation and persistent…