Inside the Daily Brief
Sep 24, 2026
A maximum-severity security vulnerability impacting SAP Commerce Cloud is witnessing active exploitation efforts. The vulnerability, tracked as CVE-2026-58231, is rated…
Microsoft is working on a security patch for the "ShieldBreak" zero-day vulnerability disclosed last week by security researcher "Nightmare Eclipse"…
AmnesiaStealer is worth a closer look because it is not just another Mac infostealer. Its operators pair ClickFix-style social engineering…
The CyberExperts Daily Brief
Get the weekday brief for people scanning the news: the developments worth a closer look, explained in about five minutes.
By subscribing you agree to our Privacy Policy. Weekday emails only.
A max-severity SAP Commerce Cloud flaw being targeted only days after patch release should move this out of routine enterprise-app…
DeadLock matters because Microsoft is describing more than another ransomware name. The operation uses decentralized infrastructure for communications, negotiation, and…
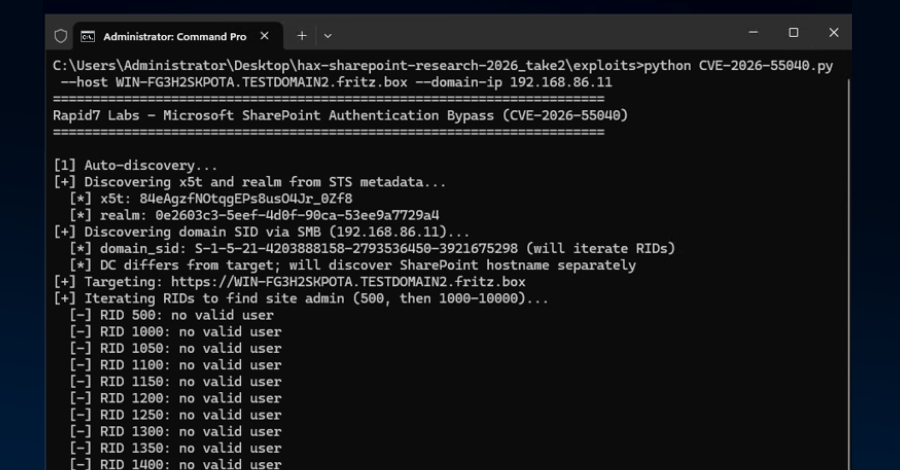
A SharePoint authentication bypass becomes much more serious once public proof-of-concept code and real exploitation arrive together. At that point,…
A Lazarus-linked Windows zero-day is not routine vulnerability noise. It is the kind of story that forces defenders to treat…
Microsoft Threat Intelligence examines DeadLock ransomware, an emerging financially motivated operation distinguished by its use of decentralized infrastructure to support…
A recently patched critical vulnerability (CVE-2026-59310) in VMware vCenter Syslog Server is being exploited in an active campaign to deploy…
Threat actors have begun to exploit a newly disclosed Microsoft SharePoint vulnerability following the release of a proof-of-concept (PoC) code.…
Microsoft has released security patches to address a Windows zero-day vulnerability known as "LegacyHive," disclosed after the July 2026 Patch…
The North Korean threat actor known as Lazarus Group has been attributed to the zero-day exploitation of a newly patched…
This is not just another catalog update. CISA is effectively telling defenders that these flaws have crossed from known problem…