What Microsoft Described
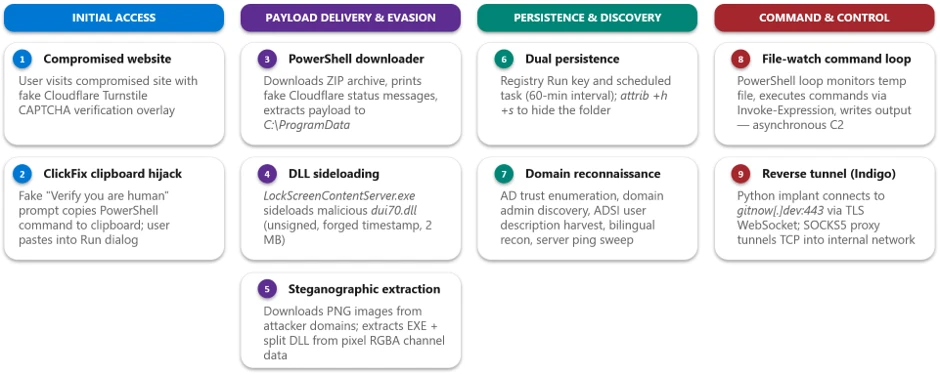
Microsoft Threat Intelligence says the TerminalFix campaign uses fake CAPTCHA-style prompts to convince users to run malicious instructions, then chains DLL sideloading with a reverse tunnel to establish more durable access.
That progression matters. Too many ClickFix discussions stop at 'user ran a command.' Microsoft's write-up is more useful because it tracks what happens after that moment, including the multistage intrusion logic and the operational purpose of the tunnel.
Why The Reverse Tunnel Changes The Story
A reverse tunnel is not just another payload feature. It gives the operator a cleaner route back into the environment, helps bypass some inbound access restrictions, and can preserve control even when the initial delivery chain was noisy or brittle.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Combined with DLL sideloading, the campaign looks less like opportunistic nuisance malware and more like a practical access operation designed to stay useful after the first stage succeeds.
The Real Defensive Problem
The hardest part here is the trust boundary between browser content and local execution. A fake verification prompt can still defeat organizations that rely mainly on user caution while lacking strong command-line telemetry, browser hardening, or endpoint controls that make the follow-on stages noisy.
Microsoft's emphasis on detections and hunting guidance is the right clue for readers. This is not a story to file under awareness training alone. It belongs equally in endpoint detection, proxy visibility, PowerShell or script execution review, and egress monitoring.
- Hunt for users launching suspicious commands from browser-mediated prompts, especially where command-line activity immediately precedes DLL sideloading or outbound tunneling behavior.
- Review whether endpoint tooling can distinguish benign remote-support patterns from reverse-tunnel establishment on workstations.
- Check browser and web-filtering controls for the fake CAPTCHA and prompt-driven execution pattern rather than assuming phishing protections alone will catch it.
- Use Microsoft's published detections and hunting guidance to tune existing analytics instead of waiting for a generic malware signature to do the job.
- Brief help desk and user-support teams so employees who report strange verification or CAPTCHA prompts are treated as possible security events, not simple browsing nuisances.
Why This Campaign Deserves Attention
ClickFix keeps working because it turns social engineering into a low-friction endpoint execution path. What makes TerminalFix worth covering is that the post-execution chain appears disciplined enough to support real operator access, not just commodity malware spray.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
The practical lesson is that defenders should evaluate these campaigns by their full intrusion path. If the first stage lands, how quickly can the attacker stabilize access, hide in normal processes, and communicate out?
Source Context
CyberExperts used Microsoft Security's reporting as the primary source for this article and preserved the pieces defenders need most: the fake CAPTCHA delivery method, the DLL sideloading stage, the reverse-tunnel component, and Microsoft's detection and hunting guidance.
Related In The Daily Brief
See this item in The 5-Minute Cyber Brief
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
Coder’s registry infrastructure compromised to push malicious modules
The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no longer verifying...
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes defenders already...
HPE patches critical ArubaOS-CX remote code execution flaw
ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation arrives. A...
Monday’s brief: GlobalProtect logins without passwords, then SonicWall, AhsayCBS and NetScaler
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.