Cyber News

Daily coverage of exploited vulnerabilities, breaches and patches, with what to do first.

Inside the Daily Brief
A real sample of the weekday read

Hackers exploit critical Adobe Commerce flaw to hijack customer accounts

Hackers exploit critical Adobe Commerce flaw to hijack customer accounts

Attempts to exploit CVE-2026-71362 in Adobe Commerce and Magento have already been detected, and the flaw appears to let attackers…

Lazarus hackers exploited Windows zero-day to target defense firms

Lazarus hackers exploited Windows zero-day to target defense firms

North Korean hackers have been exploiting CVE-2026-68820, a Windows AFD.sys privilege-escalation flaw, to target defense-sector firms as part of Operation…

Researchers Disclose AI-Assisted SharePoint Exploit Chain Reaching Unauthenticated RCE

Researchers Disclose AI-Assisted SharePoint Exploit Chain Reaching Unauthenticated RCE

Rapid7 disclosed an AI-assisted SharePoint chain pairing JWT auth bypass CVE-2026-55040 with BCS RCE CVE-2026-63520 for unauthenticated code execution on-premises.…

The CyberExperts Daily Brief

Keep up with the cyber news that changes the day

Get the weekday brief for people scanning the news: the developments worth a closer look, explained in about five minutes.
CISA Adds Three Known Exploited Vulnerabilities to Catalog

CISA Adds Three Known Exploited Vulnerabilities to Catalog

CISA's latest KEV update is only useful if it changes what defenders do next. This one adds three actively exploited…

Why metaphor may dictate your security strategy

Why metaphor may dictate your security strategy

Talos's Martin Lee argues that whether AI sandbox escapes are framed as innovation, safety or industrial accident will shape how…

Cisco warns of ASA and FTD VPN flaw exploited to crash devices

Cisco warns of ASA and FTD VPN flaw exploited to crash devices

Cisco says attackers are exploiting CVE-2026-20349, an unauthenticated flaw that crashes ASA and FTD devices with remote-access VPN enabled. There…

Microsoft August 2026 Patch Tuesday fixes 400 flaws, 3 zero-days

Microsoft August 2026 Patch Tuesday fixes 400 flaws, 3 zero-days

Microsoft's August 2026 Patch Tuesday is not just a volume story. Teams should start with the actively exploited AFD.sys zero-day,…

ChainDrop: Inside a Self-Propagating npm Worm

ChainDrop: Inside a Self-Propagating npm Worm

Unit 42 on the ChainDrop npm worm: CI runner memory scraping, cross-linked VS Code and Claude Code persistence, Ethereum-based C2…

OpenAI Launches GPT-5.6-Cyber with Reduced Safeguards for Exploit Development

OpenAI Launches GPT-5.6-Cyber with Reduced Safeguards for Exploit Development

OpenAI released GPT-5.6-Cyber through its Daybreak Red tier, a model with reduced refusals for exploit development that completed 95% of…

CISA: Microsoft SharePoint flaw now exploited in ransomware attacks

CISA: Microsoft SharePoint flaw now exploited in ransomware attacks

CISA now flags SharePoint deserialization RCE CVE-2026-45659 as exploited by ransomware gangs. Fixed in May and in KEV since July…

Kimsuky Builds Offline AI Stack to Boost Phishing and Automate Malware Development

Kimsuky Builds Offline AI Stack to Boost Phishing and Automate Malware Development

Genians says Kimsuky is running local AI tools such as Ollama and GPT4All and collecting libraries to build AI into…

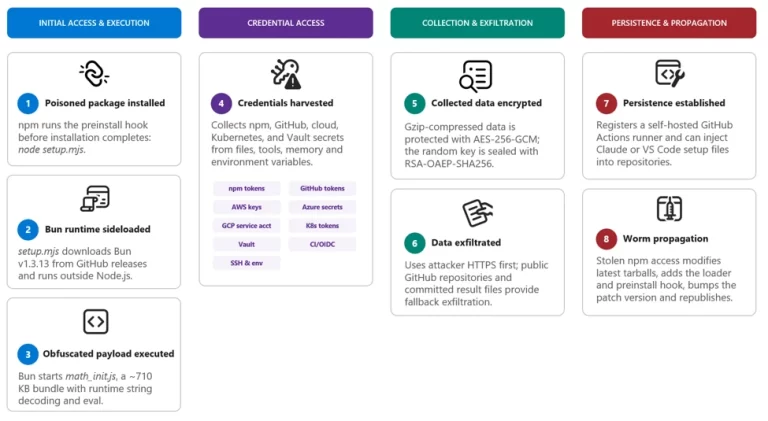
ChainDrop supply chain compromise: Anatomy of a self-propagating worm

ChainDrop supply chain compromise: Anatomy of a self-propagating worm

Microsoft's analysis of the ChainDrop npm worm: stolen maintainer credentials, CI-aware execution, credential abuse across npm, GitHub, AWS, Kubernetes and…

New Passkey Attacks Can Recover Synced Private Keys or Bypass Phishing-Resistant MFA

New Passkey Attacks Can Recover Synced Private Keys or Bypass Phishing-Resistant MFA

SpecterOps, Unit 42 and Dirk-jan Mollema showed passkey attacks that reuse logged signatures (CVE-2026-34348), recover Google-synced private keys, or borrow…