Published: 09/11/26 Today’s pattern is management-plane root: when the systems that configure firewalls, terminate VPN, and run ERP kernels become…
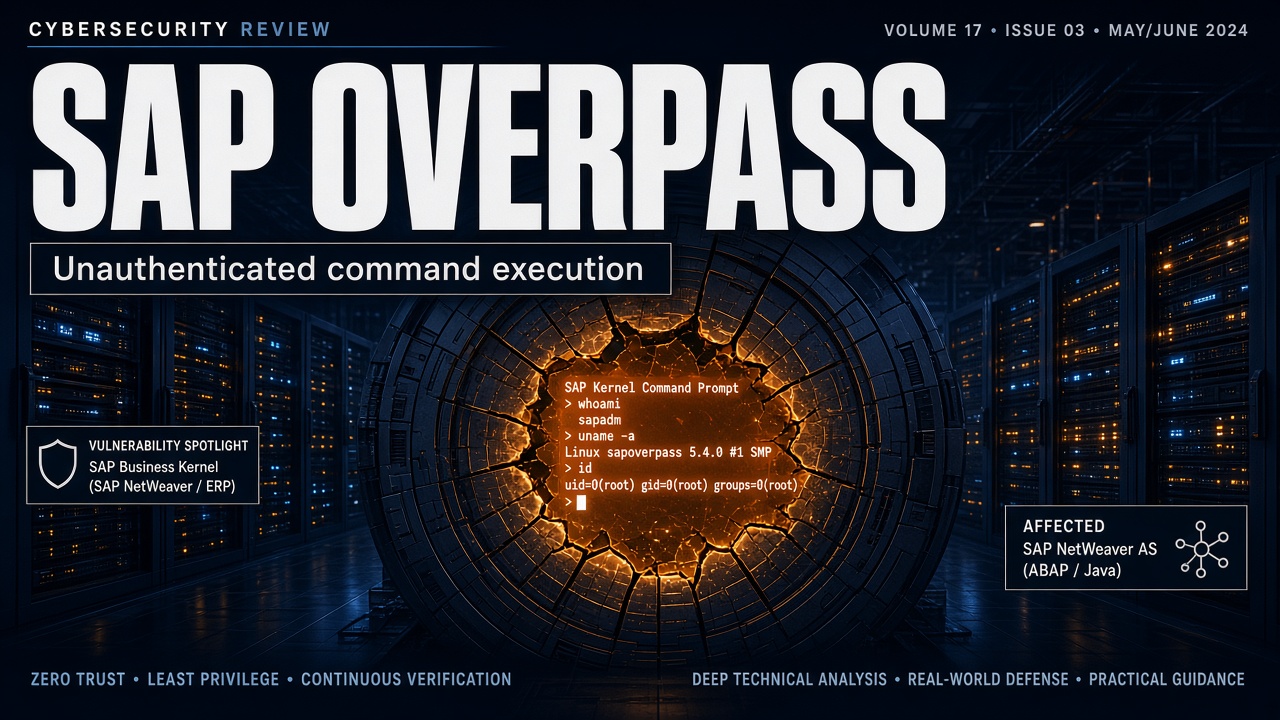
What Changed SAP’s September 2026 Patch Day, with Onapsis Research Labs, shipped Security Note 3747649 for OVERPASS (CVE-2026-44756): a memory-corruption…
What Changed Check Point disclosed on September 9, 2026 two critical flaws in VPN certificate handling on Quantum Security Gateway…
What Changed SOCRadar reports that Russian-speaking cybercrime actors have been exploiting CVE-2025-25249—an unauthenticated heap-based buffer overflow in the FortiOS and…
What Changed Cisco Talos confirmed on September 9–10 that three intrusion clusters are actively abusing Cisco Secure Firewall Management Center…
BlueMoon’s shared Chrome kit, Kestra’s suffix-match RCE, LiteLLM’s empty MCP session, and Windows Update Stack’s SYSTEM zero-day....
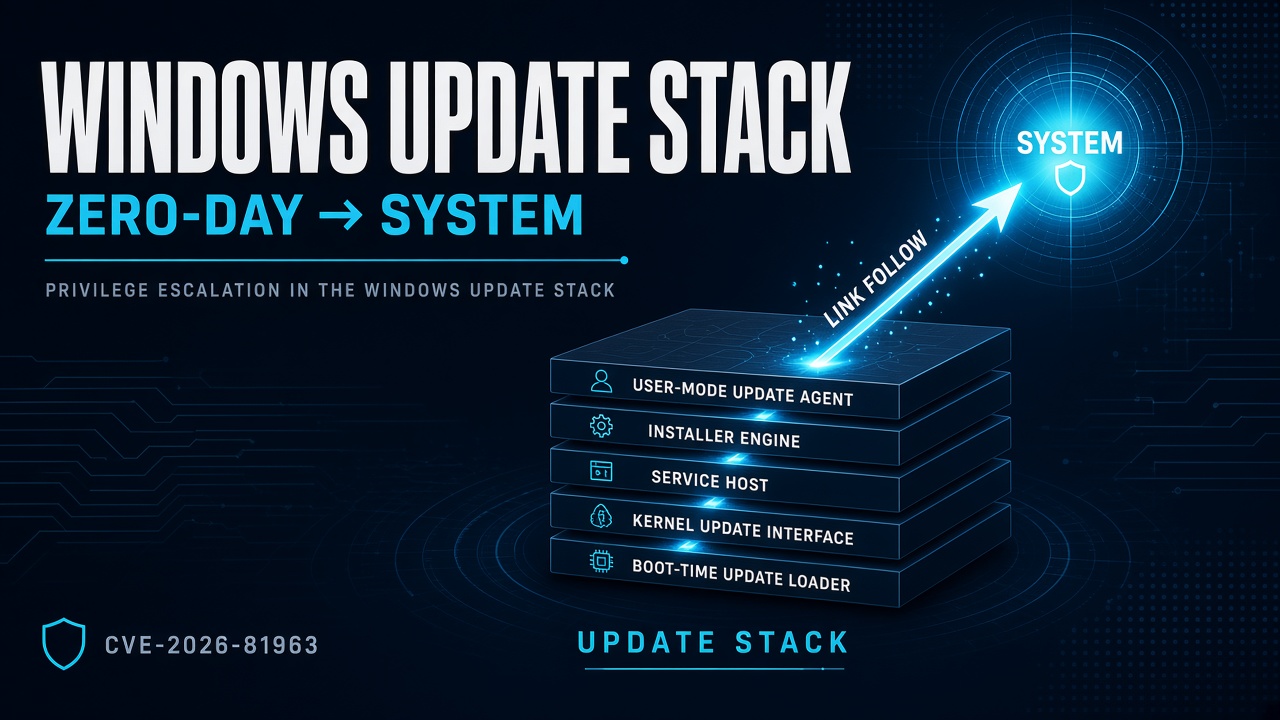
September Patch Tuesday’s exploited Update Stack EoP turns a low-privilege foothold into SYSTEM—and it is already in KEV....
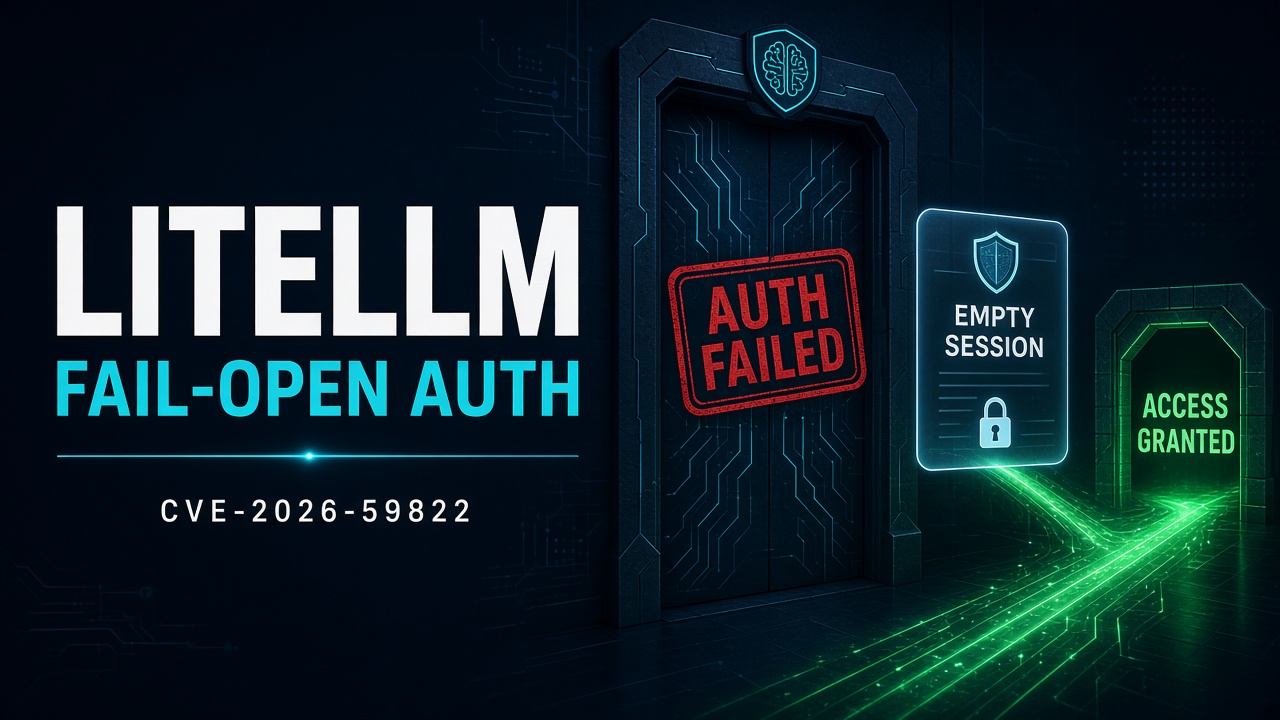
Before 1.84.0, LiteLLM’s MCP path could replace a failed Bearer check with an empty UserAPIKeyAuth()—and CISA put it in KEV....
CVE-2026-49869 (CVSS 10.0) lets unauthenticated attackers bypass Kestra Basic Auth with any path ending in /configs and run root workflows....
Proofpoint’s BlueMoon kit chains Chromium patch-gap RCE with a Windows ALPC LPE—and four espionage clusters adopted it in days....
Legacy software often operates under the “if it isn’t broken, don’t fix it” mentality until a security crisis forces action.…
Key Takeaways Container image vulnerabilities have become one of the most frustrating problems in modern software delivery. A team can…
The virtual CISO market has changed. A few years ago, many companies hired a vCISO mainly to prepare for SOC…