Updated September 2026. Encryption protects confidentiality for web traffic, messaging, cloud storage, payments, healthcare systems, and identity workflows. You do not need to be a cryptographer to choose wisely—but you do need an accurate picture of what is current, what is migrating toward post-quantum standards, and what belongs only in a legacy or museum stack.
No single algorithm solves every problem. Modern systems combine fast symmetric encryption for bulk data, asymmetric cryptography for key establishment and signatures, and separate hash functions for integrity. This guide covers the methods organizations actually encounter in 2026, how TLS 1.3 frames cipher choice, NIST’s finalized post-quantum standards, and clear retirement guidance for algorithms that older articles still list as “common.”
What encryption is (and is not)
Per NIST’s Computer Security Resource Center glossary, encryption is the cryptographic transformation of data (plaintext) into a form (ciphertext) that conceals the data’s original meaning so it cannot be known or used without authorization. When the transform is reversible, decryption restores the original plaintext.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Cryptography is broader than encryption. It includes encryption, decryption, digital signatures, key establishment, and related constructions. Classic goals include confidentiality, integrity, authentication, non-repudiation, and secure key exchange.
Hashing is not encryption. A cryptographic hash (for example SHA-256 or SHA-3) produces a fixed-length digest. It is designed to be one-way: you cannot “decrypt” a hash back to the input. Hashes support integrity checks, password storage (with a proper password-hashing function such as Argon2 or bcrypt—not bare SHA alone), digital signatures, and key derivation. Treat hashing as related cryptography, not as a substitute for encrypting data at rest or in transit.
Two main encryption categories
Symmetric encryption
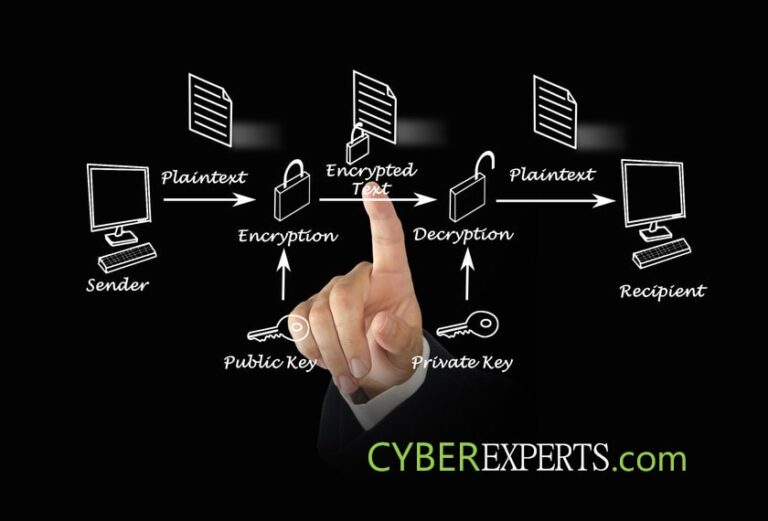
Symmetric (secret-key) cryptography uses the same key to encrypt and decrypt. It is typically far faster than public-key operations, which makes it the default for encrypting large volumes of data once a shared key exists—disk volumes, database fields, VPN payloads, and TLS record protection after the handshake.
The hard part is key distribution and lifecycle: anyone who holds the key can read the data. Production systems therefore establish keys with authenticated key exchange (or wrap them under another key) rather than emailing secrets. Prefer standard modes that provide authenticated encryption with associated data (AEAD)—confidentiality plus integrity—over older “encrypt-then-hope” constructions.
Asymmetric encryption (public-key cryptography)
Asymmetric cryptography uses a key pair: a public key that can be shared and a private key that must stay secret. Typical uses are key establishment (agreeing on a shared secret over an untrusted network), digital signatures, and encrypting small secrets (for example wrapping a symmetric key). Public-key operations are slower, so real protocols almost always use them to bootstrap a symmetric session key rather than to encrypt whole files.
Today’s widely deployed public-key schemes (RSA, elliptic-curve Diffie–Hellman and signatures) remain important in production. They are also in scope for post-quantum migration because a future cryptographically relevant quantum computer could break many of the hard problems they rely on. Plan crypto agility now; see the PQC section below.
Modern methods you should actually use
These are the constructions that dominate secure defaults in 2026 libraries, browsers, operating systems, and cloud services.
AES (especially AES-GCM)
The Advanced Encryption Standard (AES), specified in FIPS 197, is the dominant symmetric block cipher. Key lengths of 128, 192, and 256 bits are standardized. What matters as much as the cipher is the mode.
AES-GCM (Galois/Counter Mode, NIST SP 800-38D) is an AEAD mode: it encrypts and authenticates in one construction and is widely used in TLS, IPsec, disk encryption stacks, and application crypto. Prefer AES-GCM (or another approved AEAD) over raw ECB or unauthenticated CBC unless you have a carefully reviewed, specialized design.
When to use it: Default choice for data at rest and in transit when hardware AES acceleration is available—which it is on most modern CPUs and many security appliances.
ChaCha20-Poly1305
ChaCha20-Poly1305 is a stream-cipher AEAD standardized in IETF RFC 8439. It pairs the ChaCha20 stream cipher with the Poly1305 authenticator. TLS 1.3 and many mobile/VPN stacks support it alongside AES-GCM. It is especially useful on platforms without AES hardware acceleration, where it often outperforms AES-GCM in software.
When to use it: Prefer it when your stack already selects it (for example certain TLS cipher suites) or when you need a well-specified AEAD that does not depend on AES hardware. Do not invent your own ChaCha/Poly1305 wiring—use a maintained library.
TLS 1.3 and AEAD cipher suites
TLS 1.3 (IETF RFC 8446) redesigned record protection so that remaining cipher suites are AEAD-only. Legacy options such as 3DES and RC4 are gone from TLS 1.3. In practice, browsers and servers negotiate suites built on AES-GCM or ChaCha20-Poly1305, with modern key exchange (typically ECDHE today, increasingly hybrid/PQC-capable stacks as vendors roll them out).
Practical takeaway: Prefer TLS 1.3 end-to-end, disable obsolete protocol versions and cipher suites in configuration baselines, and treat “we still need 3DES for an old payment terminal” as a documented exception with a retirement plan—not as a current best practice.
RSA
RSA remains widely used for certificates, signatures, and some key-transport designs. Key length and padding matter: follow current guidance from your PKI, browser roots, and standards bodies; avoid outdated padding schemes and short moduli. RSA is comparatively slow and is a priority target for post-quantum transition in many inventories (especially long-lived certificates and archived ciphertext).
When to use it: Interoperability with existing PKI and protocols that still require RSA. For new greenfield designs, elliptic-curve schemes (today) and NIST PQC KEMs/signatures (migration path) are often preferred where supported.
Elliptic-curve cryptography (ECDH / ECDHE / ECDSA / EdDSA)
Elliptic-curve cryptography (ECC) provides public-key operations with smaller keys than RSA at comparable classical security levels. Common uses:
- ECDHE — ephemeral elliptic-curve Diffie–Hellman for forward-secret key exchange in TLS and messaging
- ECDSA / EdDSA — digital signatures (including widely used curves and Edwards-curve variants in modern protocols)
ECC is the workhorse of many 2026 internet protocols. Like RSA, classical ECC key exchange and signatures are not quantum-safe; include them in PQC migration inventories.
Diffie–Hellman (classical)
Diffie–Hellman (DH) and its elliptic-curve form enable two parties to agree on a shared secret over a public channel. Finite-field DH still appears in older configurations; modern deployments prefer ECDHE with carefully chosen groups. DH is a key-agreement primitive, not a bulk data cipher. Pair it with AEAD for the actual traffic encryption.
Post-quantum cryptography (PQC) — migrate with official NIST names
In August 2024, NIST finalized its first three post-quantum Federal Information Processing Standards. Use the official standardized names (not only the older submission nicknames):
- ML-KEM (FIPS 203; derived from CRYSTALS-Kyber) — primary module-lattice key-encapsulation mechanism for establishing shared secrets that then protect data with symmetric crypto
- ML-DSA (FIPS 204; derived from CRYSTALS-Dilithium) — primary module-lattice digital signature algorithm
- SLH-DSA (FIPS 205; derived from SPHINCS+) — stateless hash-based signature algorithm intended as a diversified backup to ML-DSA
NIST selected FALCON for standardization as FN-DSA (planned FIPS 206). As of this update, FIPS 206 remains in development on NIST’s PQC project pages—do not treat FN-DSA as a finished FIPS peer of 203–205 until NIST publishes it.
In March 2025, NIST selected HQC as an additional KEM based on different mathematics (error-correcting codes) to back up ML-KEM. NIST has stated organizations should continue migrating to the 2024 standards now; HQC is a future backup standard (draft/finalization timeline per NIST announcements), not a reason to wait.
Migration note: Inventory where you use RSA/ECC for key establishment and signatures; prioritize systems that protect long-lived secrets (“harvest now, decrypt later” risk), high-value infrastructure, and products you sell to customers who will demand PQC. Prefer vendor and open-source stacks that advertise crypto agility and support for ML-KEM/ML-DSA. CISA maintains a Post-Quantum Cryptography initiative with federal and critical-infrastructure migration resources.
Legacy and historical algorithms (do not treat as current defaults)
Older “top 10 encryption” lists often present the following as everyday choices. In 2026 they belong in a legacy, interoperability, or history section—not in a greenfield design.
DES and Triple DES (3DES / TDEA)
DES (Data Encryption Standard) used a 56-bit key and has been obsolete for decades; FIPS 46-3 was withdrawn in 2005.
Triple DES (3DES / TDEA) applied DES-style operations with multiple keys as an interim bridge to AES. NIST SP 800-131A Rev. 2 deprecated TDEA for applying cryptographic protection through 2023 and disallowed that use after December 31, 2023. NIST withdrew SP 800-67 Rev. 2 (the TDEA recommendation) on January 1, 2024. Legacy decryption of already-protected data may still be needed; new encryption with 3DES is not an approved modern choice.
Bottom line: 3DES is not a common current encryption choice for new systems. If you still see it in payment or industrial gear, schedule replacement.
IDEA and RC6
IDEA (International Data Encryption Algorithm) and RC6 are historical block ciphers. RC6 was an AES finalist that was not selected. Neither is a mainstream default in modern TLS stacks, OS disk encryption, or cloud KMS offerings. Keep them out of “recommended methods” lists unless you are documenting a specific legacy product.
Blowfish and Twofish
Blowfish and its relative Twofish (another AES finalist) appear in older software and some niche tools. They are not the current recommended general-purpose algorithms for new designs; prefer AES-GCM or ChaCha20-Poly1305 via supported libraries.
ElGamal
ElGamal is a classical public-key scheme related to Diffie–Hellman. It is important historically and still appears in some ecosystems, but it is not the usual first pick for new internet-facing systems compared with modern ECDH/EdDSA stacks and emerging PQC KEMs.
When to use what (quick guide)
- Encrypting data in transit (websites, APIs): TLS 1.3 with AEAD cipher suites (AES-GCM or ChaCha20-Poly1305).
- Encrypting data at rest: AES-GCM (or platform disk/volume encryption built on AES) with sound key management (KMS/HSM, envelope encryption).
- Messaging / constrained devices without AES hardware: ChaCha20-Poly1305 where your protocol already standardizes it.
- Certificates and signatures (classical): Follow your PKI; ECDSA/EdDSA or RSA as required for interoperability—while planning PQC signatures (ML-DSA / SLH-DSA).
- Key establishment facing quantum risk: Plan for ML-KEM (and hybrid classical+PQC modes as vendors ship them); track HQC as a future backup, not a delay.
- Integrity only: Use a cryptographic hash or HMAC/AEAD tag—do not call hashing “encryption.”
- Legacy 3DES/IDEA/RC6/DES: Decrypt/migrate only; do not deploy for new protection.
Implementation hygiene
- Use vetted libraries (OS crypto APIs, OpenSSL/BoringSSL, libsodium, cloud KMS). Do not implement AES, GCM nonces, or RSA padding yourself.
- Protect keys with least privilege, rotation, hardware-backed storage where warranted, and envelope encryption for bulk data.
- Prefer AEAD so ciphertext cannot be silently flipped.
- Build crypto agility so algorithm swaps (including PQC) do not require rewriting the business application.
- Inventory first for PQC—CISA and NIST both emphasize discovery of vulnerable cryptography before wholesale replacement.
Sources
- NIST CSRC glossary — Encryption: csrc.nist.gov/glossary/term/encryption
- FIPS 197 — Advanced Encryption Standard (AES): csrc.nist.gov/pubs/fips/197/final
- NIST SP 800-38D — GCM and GMAC: csrc.nist.gov/pubs/sp/800/38/d/final
- IETF RFC 8439 — ChaCha20 and Poly1305: rfc-editor.org/rfc/rfc8439
- IETF RFC 8446 — TLS 1.3: rfc-editor.org/rfc/rfc8446
- NIST — First three finalized PQC standards (ML-KEM, ML-DSA, SLH-DSA): nist.gov news (Aug 2024)
- FIPS 203 / 204 / 205: doi.org/10.6028/NIST.FIPS.203 · FIPS 204 · FIPS 205
- NIST PQC project (includes FIPS 206 / FN-DSA status): csrc.nist.gov/projects/post-quantum-cryptography
- NIST — HQC selected as additional KEM (Mar 2025): nist.gov news (Mar 2025)
- NIST — Withdrawal of SP 800-67 Rev. 2 (TDEA/3DES): csrc.nist.gov news
- CISA — Post-Quantum Cryptography Initiative: cisa.gov/topics/risk-management/quantum
FAQ
Is AES-256 still the default recommendation?
Yes for symmetric encryption at rest and in transit (inside TLS). Key management and implementation mistakes matter more than algorithm shopping.
When should teams worry about post-quantum crypto?
Start inventorying long-lived secrets and TLS termination points now. Migrate when your vendors ship stable PQC options — do not roll your own.
What is the most common encryption failure?
Keys and certificates treated as afterthoughts: hard-coded secrets, expired TLS, and shared admin passwords around HSMs.
Does encryption stop ransomware?
It protects confidentiality. Availability still needs backups, identity hardening, and detection.
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
Asymmetric Encryption Example: RSA Explained Step by Step
A step-by-step asymmetric encryption example using small-number RSA, plus how public keys work in TLS 1.3, digital signatures, SSH and email, 2026...
How to Encrypt Your Internet Connection: 7 Methods That Work
How to encrypt your internet connection in 2026: force HTTPS, encrypt DNS, secure Wi-Fi with WPA3, use a trustworthy VPN or iCloud...
Why Hardware Encryption is Not Secure
Hardware Encryption is not Secure A Little History... In the past, it was assumed that hardware encryption is far more secure than...
Friday’s brief: FortiMail due Saturday, then BoKS, vm2, Satellite
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.