The 5-Minute Cyber Brief
Good morning. Today’s lead is a prompt-injection trick hidden in "Ask AI" buttons. After that: a SharePoint breach at Switzerland's federal IT office, a CPU attack that gets past Spectre v2 fixes, a KVM guest escape and a ransomware chain Microsoft says Defender stopped in 128 seconds.
Lead Story
AI Recommendation Poisoning: How "Ask AI" Buttons Silently Alter LLM Memory

A new class of prompt injection is spreading across commercial websites. It needs no malware, stolen credentials or zero-day. Instead it abuses pre-filled deep links, a standard feature in almost every major AI assistant. The researchers say they found production websites embedding hidden prompt injection payloads inside "Ask AI" buttons on marketing and competitor comparison pages.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Why marketers and buyers should care: Companies are adding AI referral buttons before deciding how far to trust the prompts behind them or how to disclose them. A page that can quietly write to an assistant’s memory can also shape what that assistant recommends weeks later.
Read more on CyberExperts: Read more on CyberExperts
Original source: The Hacker News
Also Worth Your Attention
Swiss government SharePoint breach compromised 200 accounts
Switzerland's federal IT office says hackers exploited vulnerabilities to breach its Microsoft SharePoint servers and compromised approximately 200 accounts.
Beyond the servers: With about 200 accounts involved, the cleanup covers identity and document access too. That work is slower in government, where those accounts reach regulated data.
Read more on CyberExperts: Read more on CyberExperts
New TONTOU CPU attack bypasses Spectre v2 fixes, leaks Linux password hashes
Researchers found a way to bypass recent mitigations for Spectre v2 speculative execution side-channel attacks and developed an exploit to leak secrets from Linux machines.
For shared Linux hosts: The exploit pulls real password hashes, so this is no longer a lab curiosity. If you run shared Linux machines, check which Spectre v2 mitigations are actually active and which workloads share a CPU.
Read more on CyberExperts: Read more on CyberExperts
New Zapscape KVM Flaw Could Let Privileged L1 Guest Code Escape to Linux Hosts

A newly disclosed KVM issue dubbed Zapscape could let an attacker with kernel privileges inside a nested guest break isolation and execute code on the Linux host, putting environments that expose nested virtualization to untrusted workloads in the spotlight.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
For nested virtualization: Most teams treat the hypervisor boundary as settled. Cloud and lab setups that let untrusted workloads run nested guests should ask whether they still need that feature on.
Read more on CyberExperts: Read more on CyberExperts
128 Seconds to disruption: Microsoft Defender stops ransomware at QNET
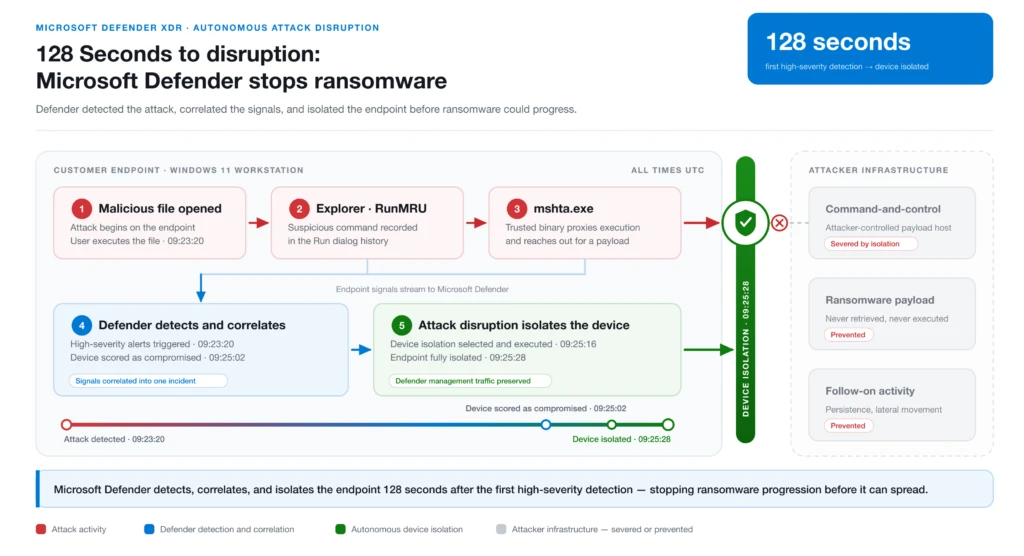
Microsoft says Defender isolated a compromised QNET endpoint in 128 seconds, interrupting a multi-stage ransomware chain before the payload could establish persistence or spread.
Speed decided it: The chain stopped at one endpoint because isolation happened before the payload could persist or spread. How fast you can isolate a machine and lock its identity often decides whether one infection turns into an outage.
Read more on CyberExperts: Read more on CyberExperts
Go Deeper
Editorial Promise
We keep the brief short. Each item says what changed and who it affects, with a link if you want the full story.
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
Coder’s registry infrastructure compromised to push malicious modules
The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no longer verifying...
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes defenders already...
HPE patches critical ArubaOS-CX remote code execution flaw
ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation arrives. A...
Monday’s brief: GlobalProtect logins without passwords, then SonicWall, AhsayCBS and NetScaler
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.