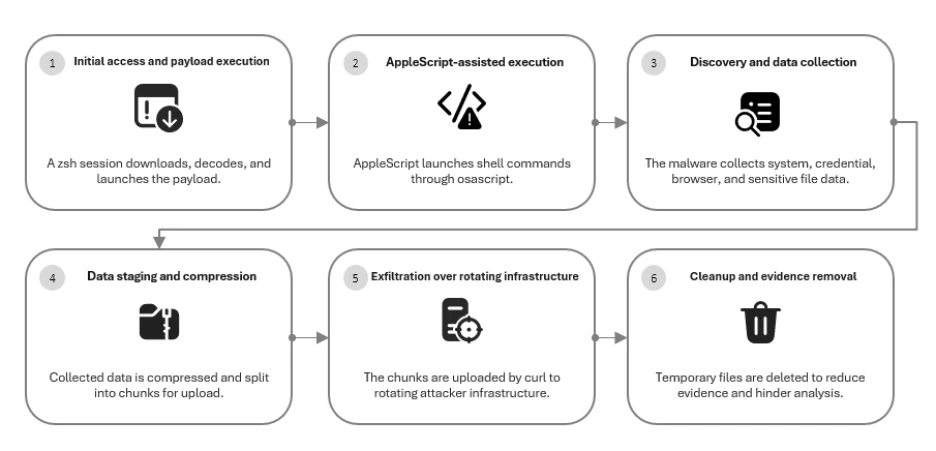
Microsoft says MacSync Stealer keeps rotating domains and delivery hosts, but it reuses the same AppleScript-assisted collection and exfiltration patterns, which helped researchers identify more than 30 related domains.
For defenders, the useful takeaway is that the infrastructure may churn quickly while the malware's operating habits stay recognizable enough to hunt.
What To Know
According to Microsoft, the reliable pivots were not flashy indicators. They were repeatable behaviors around AppleScript-assisted execution, data collection, local staging, compression, exfiltration, and cleanup.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
That matters because it gives defenders something sturdier than a one-domain blocklist. If the infrastructure keeps changing but the collection and exfiltration workflow stays familiar, behavioral detection can outlast the current domain set.
Why CyberExperts Flagged It
Mac-focused infostealer coverage still gets treated as secondary too often, especially in mixed-device fleets where Windows telemetry dominates the day-to-day workflow.
The more useful lesson here is that disposable infrastructure does not make a campaign untraceable. It just means teams have to anchor detections to the behaviors that survive each rebuild.
What Defenders May Be Underestimating
Teams may underestimate how much low-friction scripting and archive staging can reveal before a confirmed malware verdict ever lands.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
If you only look for known domains, you are playing the attacker's game. If you also watch for unusual AppleScript use, local archive creation, and suspicious outbound patterns from Macs, you get a better chance to catch the next infrastructure turn too.
What Teams Should Do Next
- Hunt for AppleScript-driven collection or execution activity on managed Macs, especially where it is paired with unusual child processes or data access.
- Review endpoint telemetry for temporary archive staging, compression, and outbound transfers to recently registered or low-reputation domains.
- Track the Microsoft research for newly identified infrastructure and use it to tune detections around behaviors, not just the published domains.
Source Context
Source: Microsoft Security.
Related In The Daily Brief
See this item in The 5-Minute Cyber Brief
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
Coder’s registry infrastructure compromised to push malicious modules
The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no longer verifying...
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes defenders already...
HPE patches critical ArubaOS-CX remote code execution flaw
ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation arrives. A...
Monday’s brief: GlobalProtect logins without passwords, then SonicWall, AhsayCBS and NetScaler
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.