The 5-Minute Cyber Brief
Good morning. Start with CISA’s KEV move on two exploited PaperCut flaws, because this is the kind of update that changes patch order immediately. Then move through the identity-pressure stories that show how Teams abuse, trusted channels, and ClickFix tradecraft keep turning ordinary workflow into attacker leverage.
Lead Story
CISA Adds Two Known Exploited Vulnerabilities to Catalog

CISA added two exploited PaperCut NG/MF flaws to KEV on August 31: CVE-2026-81578, missing authentication for a critical function, and CVE-2026-82078, unsafe reflection.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Why it matters: Print management servers often have loose ownership and broad network reach.
Recommended action: Find every PaperCut server, apply the fix and restrict admin access.
Read more on CyberExperts: Read more on CyberExperts
Original source: CISA
Also Worth Your Attention
Berlin confirms data theft after Rhysida ransomware attack claims
Berlin’s city administration confirmed data theft after the Rhysida gang listed it on its leak site. Affected departments were disconnected on August 14; Rhysida claims about 5.79 TB, or 1.44 million files.
Why it matters: Municipal networks concentrate many departments’ data, which widens the impact.
Recommended action: Check that incident plans cover notification across departments, not just IT recovery.
Read more on CyberExperts: Read more on CyberExperts
Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams
Unit 42 says the Spring Ring campaign used external Microsoft Teams accounts posing as help desk staff and follow-up voice calls to target more than 150 employees at 10 or more companies between January and April. One variant moved on to NTLM relay against domain controllers.
Why it matters: Teams messages get less suspicion than email.
Recommended action: Restrict external Teams contact and verify help-desk requests through a known channel.
Read more on CyberExperts: Read more on CyberExperts
TerminalFix campaign deploys a reverse tunnel through multistage intrusion
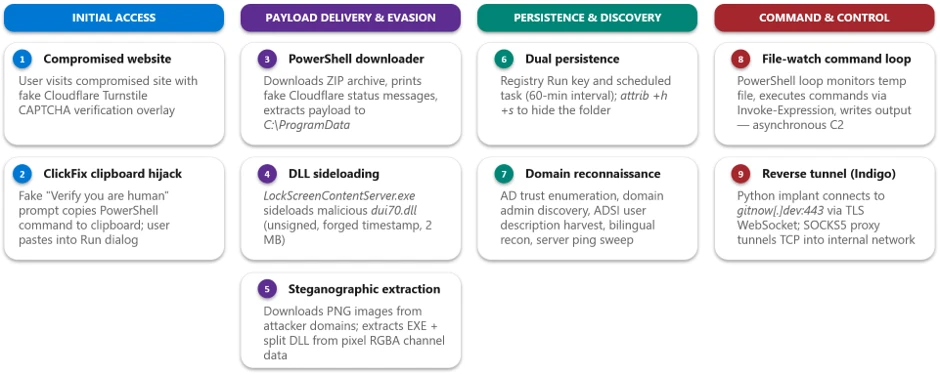
Microsoft describes TerminalFix, a ClickFix campaign that uses fake CAPTCHA prompts, DLL sideloading and a reverse tunnel for lasting access.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Why it matters: A reverse tunnel can bypass inbound firewall rules.
Recommended action: Hunt for browser-launched commands followed by DLL sideloading or new outbound tunnels.
Read more on CyberExperts: Read more on CyberExperts
Identity Abuse Through Trusted Communication Channels
Unit 42 says endpoint alerts tied to collaboration tools more than quadrupled in 12 months, and 99% of them related to chat or voice phishing. Its examples include APT29 using compromised Teams accounts and Slack webhooks used to exfiltrate credentials from VPN appliances.
Why it matters: Once an account is compromised, malicious messages look like normal work.
Recommended action: Limit external federation and guest access, and watch for unexpected outbound webhook traffic.
Read more on CyberExperts: Read more on CyberExperts
Go Deeper
Editorial Promise
CyberExperts should help you get the signal fast, understand what actually matters, and know where to go deeper before the day gets noisy.
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
Coder’s registry infrastructure compromised to push malicious modules
The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no longer verifying...
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes defenders already...
HPE patches critical ArubaOS-CX remote code execution flaw
ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation arrives. A...
Monday’s brief: GlobalProtect logins without passwords, then SonicWall, AhsayCBS and NetScaler
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.