George Bailey

George Bailey is the byline of the CyberExperts editorial desk, the team behind the CyberExperts Daily Brief. The desk covers vulnerabilities, breaches and security news from vendor advisories, CISA alerts and other primary sources, and links those sources in every story. Questions or corrections: [email protected].
Microsoft August 2026 Patch Tuesday fixes 400 flaws, 3 zero-days

Microsoft August 2026 Patch Tuesday fixes 400 flaws, 3 zero-days

Microsoft's August 2026 Patch Tuesday is not just a volume story. Teams should start with the actively exploited AFD.sys zero-day,…

ChainDrop: Inside a Self-Propagating npm Worm

ChainDrop: Inside a Self-Propagating npm Worm

Unit 42 on the ChainDrop npm worm: CI runner memory scraping, cross-linked VS Code and Claude Code persistence, Ethereum-based C2…

OpenAI Launches GPT-5.6-Cyber with Reduced Safeguards for Exploit Development

OpenAI Launches GPT-5.6-Cyber with Reduced Safeguards for Exploit Development

OpenAI released GPT-5.6-Cyber through its Daybreak Red tier, a model with reduced refusals for exploit development that completed 95% of…

CISA: Microsoft SharePoint flaw now exploited in ransomware attacks

CISA: Microsoft SharePoint flaw now exploited in ransomware attacks

CISA now flags SharePoint deserialization RCE CVE-2026-45659 as exploited by ransomware gangs. Fixed in May and in KEV since July…

The 5-Minute Cyber Brief: August 11, 2026

The 5-Minute Cyber Brief: August 11, 2026

CISA ties SharePoint CVE-2026-45659 to ransomware, LoadMaster joins KEV, OpenAI launches GPT-5.6-Cyber, the ChainDrop npm worm, and a joint advisory…

Kimsuky Builds Offline AI Stack to Boost Phishing and Automate Malware Development

Kimsuky Builds Offline AI Stack to Boost Phishing and Automate Malware Development

Genians says Kimsuky is running local AI tools such as Ollama and GPT4All and collecting libraries to build AI into…

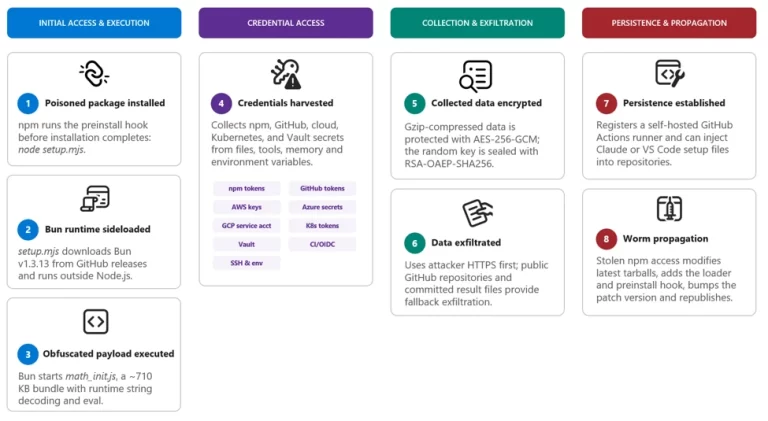
ChainDrop supply chain compromise: Anatomy of a self-propagating worm

ChainDrop supply chain compromise: Anatomy of a self-propagating worm

Microsoft's analysis of the ChainDrop npm worm: stolen maintainer credentials, CI-aware execution, credential abuse across npm, GitHub, AWS, Kubernetes and…

New Passkey Attacks Can Recover Synced Private Keys or Bypass Phishing-Resistant MFA

New Passkey Attacks Can Recover Synced Private Keys or Bypass Phishing-Resistant MFA

SpecterOps, Unit 42 and Dirk-jan Mollema showed passkey attacks that reuse logged signatures (CVE-2026-34348), recover Google-synced private keys, or borrow…

CISA: SonicWall SMA1000 flaws now exploited by ransomware gangs

CISA: SonicWall SMA1000 flaws now exploited by ransomware gangs

CISA now flags SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410 as used by ransomware; more than 380 appliances remain exposed online....

The 5-Minute Cyber Brief: August 10, 2026

The 5-Minute Cyber Brief: August 10, 2026

Metabase SQL injection zero-day used in data theft, LoadMaster CVE-2026-8037 joins KEV, Head Mare trojanizes TrueConf installers, and Talos on…

“Keep going, bro. You’ve got this!” A data-driven look at how adversaries are weaponizing AI

“Keep going, bro. You’ve got this!” A data-driven look at how adversaries are weaponizing AI

Talos studied attacker prompt logs and found that simple framing tricks got past AI guardrails, helping actors build DDoS botnets,…

128 Seconds to disruption: Microsoft Defender stops ransomware at QNET

128 Seconds to disruption: Microsoft Defender stops ransomware at QNET

Microsoft Defender attack disruption now isolates compromised endpoints automatically. In a QNET incident it cut off an mshta-based attack 128…

Hackers breach TrueConf to trojanize client installers with backdoors

Hackers breach TrueConf to trojanize client installers with backdoors

The TrueConf compromise is not just a server-breach story. It is a reminder that update channels themselves become attack infrastructure…