
.
Cyber attacks are a threat to businesses of all sizes and in all industries. The FBI received 1,008,597 cybercrime complaints with $20.9 billion in reported losses in 2025, a 26% jump in losses from 2024 (FBI IC3), so businesses are more exposed than ever to the financial and reputational repercussions of cyberattacks. Updated October 2026 with current statistics.
To help business owners prevent and respond to such incidents, this guide will go over statistics on types of cyberattacks and actionable tips to prevent them.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
Costs of Cybercrime
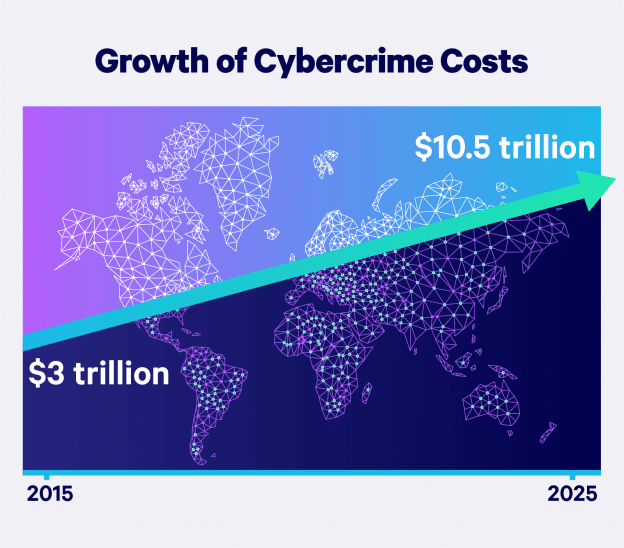
IBM’s 2026 Cost of a Data Breach Report puts the global average cost of a data breach at a record $4.99 million, up 12% from the year before. In the United States the average reached $11.5 million (IBM).
.
.
Small businesses are particularly vulnerable to cybercrime and face the most severe consequences. A study by Accenture reports that 43% of cyber attacks target small businesses, while only 14% are equipped with adequate cyber defenses.
Depending on the severity and scope of the cyberattack, it can have a serious and lasting impact on your company’s infrastructure.
In addition to financial loss resulting from cyber attacks, your business may also suffer from system downtime, damage to brand reputation, lost data and lost productivity.
For these reasons, it’s critical for businesses of all sizes to be cognizant of the impact that cyber attacks can have in order to minimize the consequences and prevent them from occurring in the first place.
Common Types of Cyber Attacks
Knowing the most common types of cyberattacks will help you develop a keen eye for suspicious activity so that you can act wisely to prevent theft and fraud.
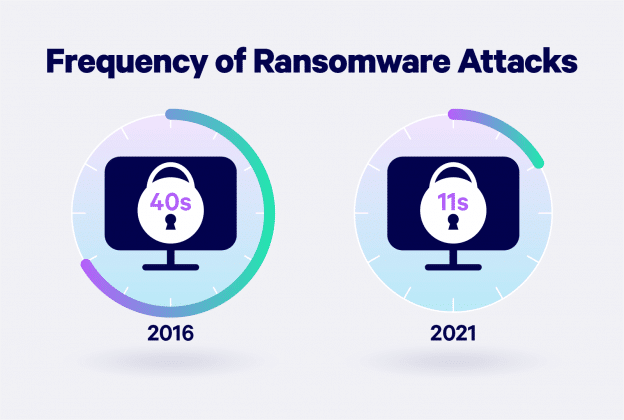
Ransomware attacks occur when malicious software is used to restrict access to a computer’s systems or data until a ransom is paid to the perpetrator. These attacks are becoming more prevalent and more advanced as technology evolves. Verizon’s 2026 Data Breach Investigations Report found ransomware in 48% of breaches, although 69% of victims did not pay and the median payment fell to $139,875.
2. Phishing
Phishing is a type of online scam that involves sending an email or other virtual communication impersonating a seemingly-reputable source, such as a bank or a government entity. These emails usually ask for personal information such as social security numbers to steal identities, money, or open new accounts in someone else’s name. Phishing and spoofing was the most reported crime type in the FBI’s 2025 Internet Crime Report, with 191,561 complaints, and business email compromise, which usually starts with a phishing or spoofed message, cost victims more than $3 billion.
3.Malware
Malware is malicious software that gets downloaded onto devices without one’s consent. It can cause devices to crash or allow hackers access to computer activity and files. Malware is often downloaded onto devices when users are prompted to click on unsecure links. Malware is often the first stage of larger attacks such as ransomware and credential theft.
Know what matters before your first meeting.
Weekday mornings. Five minutes. What changed in security, why it matters.
By subscribing you agree to our Privacy Policy.
Free. Weekday mornings. 5 minutes or less.
4.Man-in-the-Middle
A man-in-the-middle (MITM) attack occurs when a user intercepts communication between two people, or between one person and a machine. For example, a hacker might guide a user into a fraudulent site that appears to be the user’s bank’s website to collect their data. Using HTTPS everywhere, HSTS and phishing-resistant MFA greatly reduces the risk.
5.Data Breaches
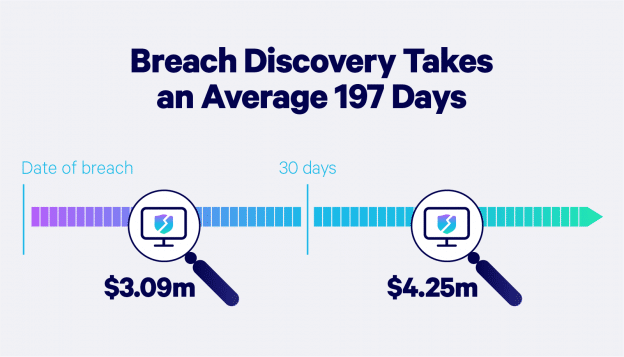
According to IBM’s 2026 report, it takes an average of 183 days to identify a breach and another 64 days to contain it, a 247-day lifecycle. Needless to say, the longer it takes to discover a security breach, the more a company’s reputation and assets suffer. That’s why it’s essential for businesses to have a data breach response plan to be prepared if a breach ever occurs.
Industry-based Vulnerabilities
While it’s important for businesses in every industry to take comprehensive measures to combat cybercrime, certain industries are at greater risk than others.
It’s within expectations that companies in industries that possess users’ personal information are the most common targets of cybercrime. These industries include:
●Financial institutions. Not only do banks and credit unions have access to users’ personal information such as addresses and contact details, but they also manage financial assets and credit card numbers.●Healthcare institutions. Hospitals and other healthcare institutions safeguard sensitive patient data such as medical history, insurance information, and patient records.●Corporations. Corporations house not only data on employees and clients, but also the highly valuable intellectual property, product concepts, and contracts.
Cybersecurity Best Practices
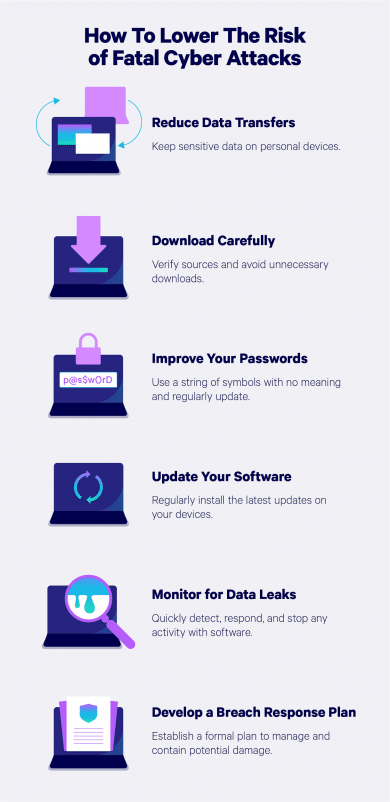
With increasing cyber threats, especially due to the rise in remote work, businesses need to be as prepared as possible to mitigate the risk of cyberattacks. Here are some cybersecurity best practices that your company should follow to strengthen security and prevent cyber attacks.
1.Minimize data transfers. In a corporate setting, it’s nearly impossible to prevent the transfer of data between devices. Be mindful of how many devices contain important data and try to make transfers as minimally as possible, especially when it comes to sensitive data.2.Verify download sources. Before making any downloads, scan the website you’re downloading from to ensure that it’s verified, and only click on legitimate download links.3.Update software regularly. Software developers are continuously updating their applications with the best available security measures, so updating your programs and devices whenever possible is a great way to protect against cyber attacks.4.Encrypt where possible. Encryption tools can be used to protect data from outsiders. When encryption isn’t possible, password protection is a great alternative. Use long, unique passphrases stored in a password manager, turn on multi-factor authentication, and change a password when there is a sign it was exposed (current NIST guidance no longer recommends forced periodic changes).5.Monitor data. Data breach monitoring tools will alert you when there is suspicious activity regarding your data. These tools will help you prevent data theft in real-time.6.Have a breach response plan. Breaches can happen to even the most prepared businesses. When they do, having a codified, organization-wide plan can help prevent further damage and speed up recovery efforts.
Cybercrime is becoming more frequent and more advanced every day, posing a threat to businesses and individuals everywhere. Rather than waiting to respond to a cyberattack, be proactive by bolstering your security measures to lower the risks of encountering an attack.
Newer CyberExperts coverage on this topic
This article still works as background. If you want the current picture, start with the freshest related coverage below and today's brief.
CMMC After the Phase 2 Suspension: What Contractors Still Have to Do in 2026
Short answer: on July 13, 2026, the Department of War suspended the move to CMMC Phase 2, which was due on November...
Blue Team Certifications (2026): CySA+, GCIA, BTL1 and SC-200 Compared
Blue team certifications compared from the issuers' own pages: CompTIA CySA+ V4, GIAC GCIA, BTL1 from Centri (Security Blue Team) and Microsoft...
Digital Forensics Certifications (2026): GCFA, CHFI, EnCE and CCE Compared
Digital forensics certifications compared from the issuers' own pages: GIAC GCFA and GCFE, EC-Council CHFI, OpenText EnCE and ISFCE CCE, with exam...
Monday’s brief: SonicWall VPN logins skip MFA, then Alpine SSH, Windows Paint and Claude Code secrets
The fastest way to catch up on what changed after this article was published.
Start your morning with the signal that matters.
Get the biggest cybersecurity developments, why they matter, and where to go deeper on CyberExperts.
By subscribing you agree to our Privacy Policy.
Free. Weekdays. Built for operators.
