The CyberExperts Daily Brief
Follow the bigger picture behind this topic with a concise weekday brief on what changed and why it matters.
By subscribing you agree to our Privacy Policy. Weekday emails only.
Cisco network gear, court-system exposure, poisoned Terraform modules, and malware riding a trusted runtime....
The Coder incident is a supply-chain lesson in miniature: once attackers can tamper with trusted module distribution, defenders are no…
The useful lesson in this campaign is not that Node.js is bad. It is that adversaries keep choosing legitimate runtimes…
ArubaOS-CX deserves attention because switching software rarely gets treated with the same urgency as identity or edge security until exploitation…
The C-Track story matters because it sits inside judicial workflow, not generic office software. When court case-management data is exposed,…
Cisco's Nexus 9000 update is the kind of network-infrastructure issue that should not wait behind normal maintenance rhythm. The core…
CISA adds ownCloud, Linux kernel and Artifactory flaws to KEV, new SonicWall SMA 1000 zero-days, Sangoma Switchvox exploited, All-in-One WP…
Cisco Talos is making a more practical point than the headline alone suggests: if defensive workflows depend on third-party AI…
The All-in-One WP Migration and Backup plugin flaw is not just another WordPress plugin headline. Wordfence says CVE-2026-19949 can let…
CVE-2026-9586 in Sangoma Switchvox is more than a generic VoIP bug. Horizon3 says the unauthenticated SQL injection in the `/pa`…
Two exploited zero-days in SonicWall SMA 1000 appliances are the kind of edge-security story that deserves faster attention than the…
CISA added ownCloud CVE-2023-49105, Linux kernel CVE-2026-53362, and JFrog Artifactory CVE-2026-66384 to the KEV catalog based on active exploitation. That…
Shadowserver counts 21,899 internet-exposed Exchange servers unpatched for CVE-2026-62911, a mailbox-takeover authentication bypass with public exploit code....
Aesto Health, which archives patient data for healthcare providers, says a December 2025 breach of its AWS environment exposed data…
Unit 42's AI-enabled malware research is useful because it separates hype from operational change. The story is not that attackers…
Attackers are exploiting Langflow RCE flaw CVE-2026-0768 to steal OpenAI and AWS keys from instances running 1.4.2 or earlier. Upgrade…
Attackers are exploiting JFrog Artifactory auth bypass CVE-2026-82329 (CVSS 9.8) to mint admin tokens and add backdoor users. Upgrade to…
ESET says UAC-0099 put a "nuclear weapon" request in VBScript malware to make AI tools refuse to analyze it. The…
CISA adds two PaperCut flaws to KEV, Berlin confirms Rhysida data theft, Spring Ring Teams vishing, TerminalFix ClickFix campaign, and…
Spring Ring is useful because it shows how collaboration platforms are becoming identity and access attack surfaces, not just communication…
Berlin's Rhysida incident matters because it shows how quickly a public-sector cyber event becomes a data-governance and continuity problem once…
CISA's latest KEV move matters because it turns two PaperCut flaws into an immediate exposure decision, not a routine backlog…
This Unit 42 research matters because it explains how identity attacks ride inside the tools employees already trust. The danger…
TerminalFix is valuable as a stand-alone story because it shows a modern ClickFix chain built for persistence, not just initial…
The McKesson disclosure is not valuable because of the raw record claim alone. It matters because it points to a…
PaperCut is warning that active exploitation now affects every NG and MF deployment, which makes this an exposure-mapping problem before…
The August 28 Cyber Brief tracks urgent Citrix and SharePoint exploitation, a critical zero-click WordPress risk, resilient GoCaracal malware, and…
Unit 42's AI-enabled malware dataset is useful because it cuts through hype with numbers: 405 samples collected, only 12 observed…
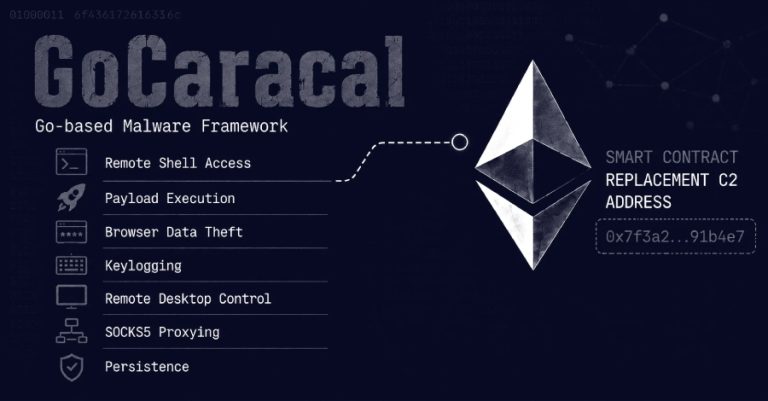
Arctic Wolf's GoCaracal research is useful because it adds specifics to the Dark Caracal story: a Go-based framework with lightweight…
CVE-2026-18431 is not a simple plugin bug. Wordfence says attackers can chain six weaknesses across the Avada theme and Fusion…
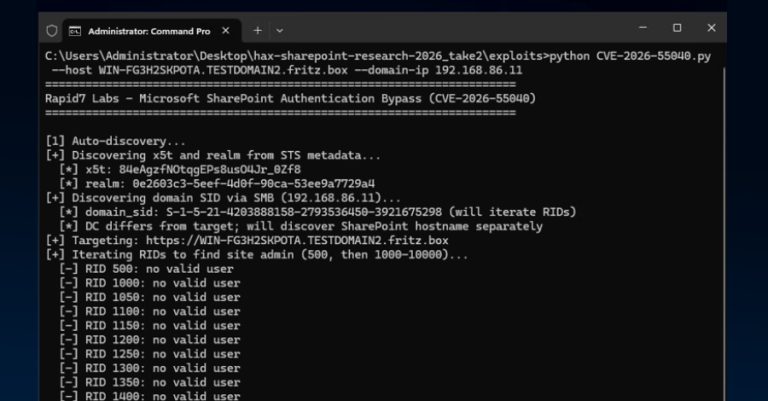
The SharePoint story is more specific than "RCE chain under attack." Defenders are now dealing with CVE-2026-55040 in the JWT…
CVE-2026-8452 is no longer a theoretical NetScaler problem. CISA has now ordered federal agencies to fix it by August 29…
The cybersecurity developments that matter most today, explained in about five minutes....
This campaign is worth attention because it moves dead-drop logic into an FTP welcome banner, which is unusual enough to…
Cisco Talos is making a strategic point that security leaders should not dismiss as thought-leadership filler. If defensive workflows depend…
AnonyMousKIT is more than another phishing-kit story because it connects stolen-device monetization to identity abuse. The useful operator detail is…
This campaign matters because the attacker is abusing trusted software-distribution infrastructure rather than only throwaway phishing sites. The useful detail…
Shadowserver found 274 Zimbra servers compromised through CVE-2026-73570 and at least 8,200 unpatched. Upgrade to ZCS 10.1.20 and hunt for…
Live Zimbra exploitation, WordPress SSO abuse, a Keycloak takeover bug, and a router flaw that punches through NAT....
Keycloak CVE-2026-18963 deserves attention because it attacks the recovery path defenders usually trust when something else goes wrong. If an…
The Calix router flaw is useful because it turns a familiar consumer and branch-office assumption upside down. NAT is often…
The miniOrange WordPress SAML issue matters because it is sitting on an identity trust boundary many site owners assume is…
CISA gave federal agencies until August 24 to patch Zimbra CVE-2026-73570, an unauthenticated SNMP command injection reachable over SMTP. Upgrade…
CISA, NSA, FBI, DOE, and EPA say actors are actively targeting Siemens S7 PLCs by scanning for internet-exposed devices and…
Expel says the campaign uses Microsoft Teams messages to push a fake "PowerShell Cleaner" MSI from Azure, then drops a…
GitLab CVE-2026-19478 is not a minor project-integrity issue. It is a 9.4 unauthenticated code-injection path against public projects, which means…
Zimbra CVE-2026-73570 exploited, GitLab CVE-2026-19478 attacked within days, CISA warns on MLflow CVE-2026-64849, and Talos on UAT-10147's AI-assisted intrusions....
Cisco Talos is describing a change in attacker workflow, not just another flashy AI label. UAT-10147 appears to be using…
MLflow is now important enough that an exposed default deployment can become a cloud-credentials problem, not just an AI-tooling problem.…
CrowdStrike's August Patch Tuesday analysis matters because it turns a wall of Microsoft CVEs into a prioritization map. The real…
CVE-2026-73570 is the kind of email-infrastructure issue that creates immediate cleanup pressure because it combines unauthenticated remote code execution with…
CISA's Gunra advisory is useful because it gives defenders more than a ransomware name. It maps how the group gets…
This story is valuable when read as a change in attack economics, not as another vague AI warning. The important…
Cisco Talos adds something the broader Patch Tuesday roundups often miss: a defender's view of which Microsoft flaws are likely…
CISA's latest KEV additions are not four unrelated patch notes. They expose four different trust boundaries already under pressure: remote…
CISA ties Windows Task Host CVE-2025-60710 to ransomware, Clop's Windchill web shell, MLflow SSRF used to steal cloud credentials, and…
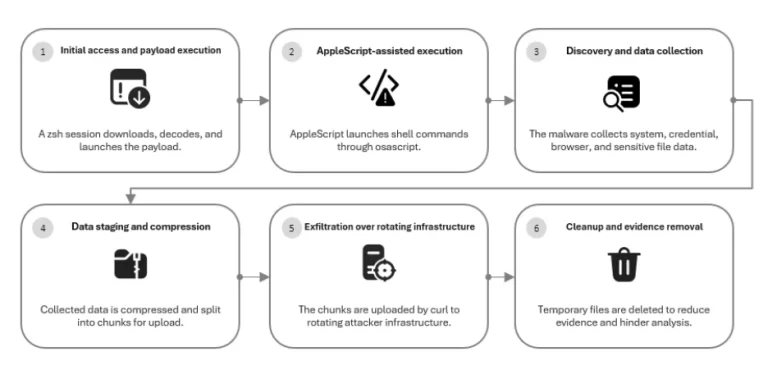
Microsoft says MacSync Stealer keeps rotating domains and delivery hosts, but it reuses the same AppleScript-assisted collection and exfiltration patterns,…
Attackers are exploiting an MLflow SSRF flaw to reach cloud metadata services and steal credentials, while a separate FUXA issue…
ReliaQuest found a custom Clop web shell for PTC Windchill and FlexPLM, used via CVE-2026-12569 to locate and steal design…
CISA now flags Windows Task Host privilege escalation flaw CVE-2025-60710, patched in November 2025, as used in ransomware attacks. Check…
ShieldBreak still unpatched, GitLab fixes critical CVE-2026-19478, Pokémon Center data exposed via CEVA, Microsoft on DeadLock ransomware, and August's network…
Pokémon Center UK and Germany customer names, addresses, phone numbers, emails and orders were exposed in the CEVA Logistics breach.…
Talos counts 421 Microsoft fixes in August 2026, with 62 critical. AFD.sys flaw CVE-2026-68820 is exploited, and WDS TFTP, SharePoint…
Attackers began probing SAP Commerce Cloud flaw CVE-2026-58231 (CVSS 10) three days after the patch. Onapsis advises patching, then rebuilding…
Microsoft is working on a patch for ShieldBreak, a public Defender zero-day (CVE-2026-69414) that bypasses the RoguePlanet fix and gives…
Microsoft prepares a fix for Defender zero-day ShieldBreak, SAP Commerce Cloud CVE-2026-58231 targeted days after patch, and August's critical DNS,…
AmnesiaStealer is worth a closer look because it is not just another Mac infostealer. Its operators pair ClickFix-style social engineering…
A max-severity SAP Commerce Cloud flaw being targeted only days after patch release should move this out of routine enterprise-app…
DeadLock matters because Microsoft is describing more than another ransomware name. The operation uses decentralized infrastructure for communications, negotiation, and…
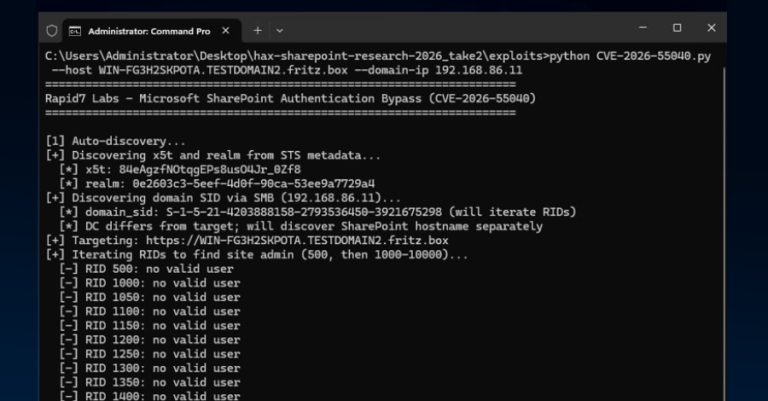
A SharePoint authentication bypass becomes much more serious once public proof-of-concept code and real exploitation arrive together. At that point,…
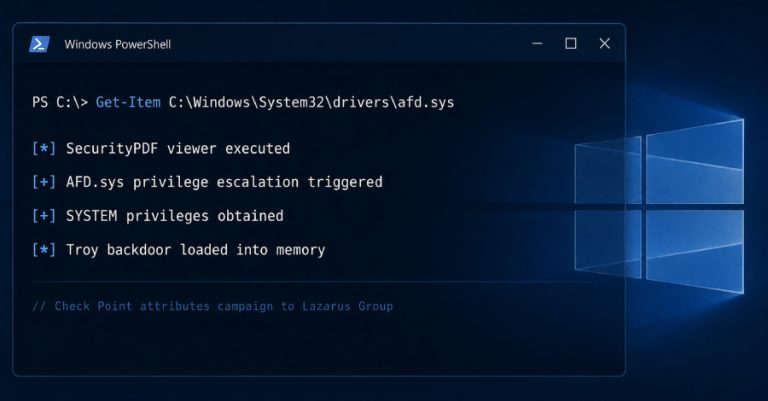
A Lazarus-linked Windows zero-day is not routine vulnerability noise. It is the kind of story that forces defenders to treat…
Lazarus uses a Windows zero-day against defense firms, Microsoft patches LegacyHive, SharePoint CVE-2026-55040 attacked after PoC, vCenter flaw used for…
Attackers are exploiting vCenter RCE flaw CVE-2026-59310 to install reverse_ssh backdoors. QUIRSO counted 361 attacking IPs in 47 countries by…
Attackers began exploiting SharePoint auth bypass CVE-2026-55040 after Rapid7 released a PoC; KEVIntel saw eight of 12 attempts on August…
Microsoft fixed LegacyHive (CVE-2026-62832), a Windows User Profile Service flaw disclosed by Nightmare Eclipse that lets a local user gain…
CISA added Cisco ASA/FTD VPN DoS CVE-2026-20349, Windows AFD.sys privilege escalation CVE-2026-68820 and Metabase SQL injection CVE-2026-72898 to KEV on…
Lazarus used AFD.sys zero-day CVE-2026-68820 against defense firms, CrowdStrike and Talos break down August Patch Tuesday, and federal KEV deadlines…
The latest LiteLLM fallout matters because the issue is no longer just a package-security anecdote: teams may still have long-lived…
DeadLock is an emerging ransomware operation that pairs double extortion with decentralized recovery and leak infrastructure, giving the actor a…
Attackers are actively exploiting CVE-2026-59310, a CVSS 9.8 directory-traversal flaw in VMware vCenter, and incident responders are seeing successful compromise…
Attempts to exploit CVE-2026-71362 in Adobe Commerce and Magento have already been detected, and the flaw appears to let attackers…
North Korean hackers have been exploiting CVE-2026-68820, a Windows AFD.sys privilege-escalation flaw, to target defense-sector firms as part of Operation…
Rapid7 disclosed an AI-assisted SharePoint chain pairing JWT auth bypass CVE-2026-55040 with BCS RCE CVE-2026-63520 for unauthenticated code execution on-premises.…
August Patch Tuesday fixes exploited AFD.sys CVE-2026-68820, CISA adds three KEV entries, Cisco ASA/FTD DoS flaw exploited, and Rapid7's AI-assisted…
CISA's latest KEV update is only useful if it changes what defenders do next. This one adds three actively exploited…
Talos's Martin Lee argues that whether AI sandbox escapes are framed as innovation, safety or industrial accident will shape how…
Cisco says attackers are exploiting CVE-2026-20349, an unauthenticated flaw that crashes ASA and FTD devices with remote-access VPN enabled. There…
Microsoft's August 2026 Patch Tuesday is not just a volume story. Teams should start with the actively exploited AFD.sys zero-day,…
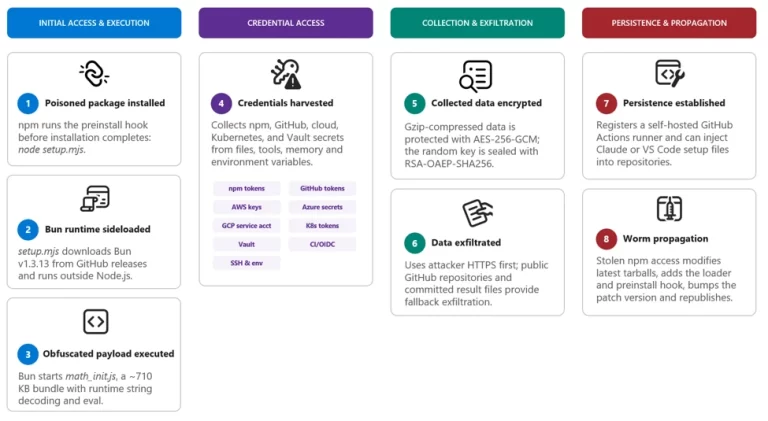
Unit 42 on the ChainDrop npm worm: CI runner memory scraping, cross-linked VS Code and Claude Code persistence, Ethereum-based C2…
OpenAI released GPT-5.6-Cyber through its Daybreak Red tier, a model with reduced refusals for exploit development that completed 95% of…
CISA now flags SharePoint deserialization RCE CVE-2026-45659 as exploited by ransomware gangs. Fixed in May and in KEV since July…
CISA ties SharePoint CVE-2026-45659 to ransomware, LoadMaster joins KEV, OpenAI launches GPT-5.6-Cyber, the ChainDrop npm worm, and a joint advisory…
Genians says Kimsuky is running local AI tools such as Ollama and GPT4All and collecting libraries to build AI into…
Microsoft's analysis of the ChainDrop npm worm: stolen maintainer credentials, CI-aware execution, credential abuse across npm, GitHub, AWS, Kubernetes and…
SpecterOps, Unit 42 and Dirk-jan Mollema showed passkey attacks that reuse logged signatures (CVE-2026-34348), recover Google-synced private keys, or borrow…
A joint FBI, CISA and partner advisory warns about Gunra, a Conti-derived ransomware-as-a-service that exploits internet-facing devices, deletes backups and…
CISA now flags SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410 as used by ransomware; more than 380 appliances remain exposed online....
Metabase SQL injection zero-day used in data theft, LoadMaster CVE-2026-8037 joins KEV, Head Mare trojanizes TrueConf installers, and Talos on…
Talos studied attacker prompt logs and found that simple framing tricks got past AI guardrails, helping actors build DDoS botnets,…